Table of Contents
For many small defense contractors, Cybersecurity Maturity Model Certification (CMMC) compliance isn't only a security problem. It's an additional job nobody in the defense industry was hired to do.
The requirements are documented, the assessment methodology is public, and the cybersecurity standards written into DFARS 252.204-7012 remain in effect. What's often missing is time, and someone who has done this before.
The stakes are concrete. Defense contracts tie award eligibility to the CMMC status a solicitation specifies, so companies that can't show it put the government contracts they rely on at risk.
That's what CMMC compliance support means in practice: outside help closing the gap between what your contracts require and what your organization can produce on its own.
The market for that help is crowded and confusingly labeled. Consultants, registered practitioners, managed service providers (MSPs), assessors, and software platforms all describe what they do as compliance support, and they aren't interchangeable.
This guide explains what support actually covers, who provides which parts, how the roles differ, and how to choose without paying twice for the same work.
TL;DR
- CMMC compliance support covers gap assessments, remediation, documentation, evidence collection, and ongoing compliance management. Few companies in the Defense Industrial Base (DIB) need all of it from one provider.
- The provider types are distinct. Registered Provider Organizations (RPOs) advise, managed service providers implement and operate, and assessors evaluate. Keeping those roles separate keeps your program defensible.
- Your CMMC level decides the scope of support you need. Federal Contract Information (FCI) means Level 1 basic safeguarding. Controlled Unclassified Information (CUI) generally means Level 2 and 110 security requirements. Under the current Phase 1, Level 1 requires an annual self-assessment while Level 2 self-assessment runs every three years. Both require annual affirmation.
- On July 13, 2026, the Department of War suspended implementation of CMMC Phase 2. Phase 1 self-assessment requirements remain in force, and the reform task force reports back in mid-September 2026.
- MotherBear gives contractors and the consultants supporting them one workspace for requirement status, evidence, documentation, and readiness, so support hours go into the work instead of the file hunt.
What Is CMMC Compliance Support?
CMMC compliance support is the outside expertise, services, and tooling a contractor uses to meet the CMMC requirements written into its Department of Defense (DoD) contracts.
The CMMC framework exists to strengthen protection of FCI and CUI throughout the defense supply chain and verify that required safeguards are actually in place.
Cyber threats to suppliers, and data breaches exposing sensitive data, are the backdrop: CMMC adds a verification mechanism, and robust cybersecurity practices are what it looks for.
Support exists because the requirements assume capacity many contractors don't have. A four-person machine shop handling CUI under DoD contracts carries the same 110 security requirements as a company with a full security team.
That gap is the whole market. The obligation to protect sensitive information doesn't scale down for smaller companies, so the help has to scale up to meet it.
Support in the defense sector has settled into a rough division of labor. Someone assesses where you stand, someone implements the technical controls, someone writes and maintains documentation, and someone keeps the whole thing current between assessments.
One provider can cover several of these functions, but a formal Level 2 certification assessment has to stay independent of recent consulting work. What matters otherwise is that every part gets covered and nobody assumes another party is handling it.
CMMC 2.0 and the Requirements You Need Support With
The CMMC requirements you need support with follow directly from your CMMC level, and your level follows from the data your contracts involve.
Under CMMC 2.0, Levels 1 and 2 are the ones most relevant to DoD contractors, with Level 3 applying to a narrower set of programs requiring protection against advanced persistent threats.
Each level sets a different bar for how you demonstrate compliance, which changes what kind of help is worth paying for.
CMMC Level 1: Basic Safeguarding for FCI
Level 1 applies to contractors handling only Federal Contract Information. It requires 15 basic safeguarding practices, verified through an annual CMMC self-assessment and an annual affirmation, with no outside assessor involved.
Support at this level can be relatively light. Contractors often handle it internally, bringing in help only to confirm their scoping and their understanding of what each practice requires.
The one trap is that Level 1 is pass or fail. Full compliance means every one of the 15 security practices is in place, with no remediation plans standing in for implemented controls.
CMMC Level 2: Protecting Controlled Unclassified Information
Contracts involving CUI generally require at least Level 2, along with all 110 security requirements from the National Institute of Standards and Technology (NIST) standard 800-171, Revision 2 under the current program.
This is where outside support often becomes more valuable. The cybersecurity controls span technology, written policy, personnel practices, and physical protection, and a substantial part of the work is documentation rather than technology.
The reasoning behind the stricter bar is national security. CUI is government information that requires safeguarding under law, regulation, or government-wide policy, and limiting who can gain access to it is why prime contractors flow these obligations down their supply chains.
Level 2 is also where the cost of getting it wrong changes. The obligation reaches contractors through the Defense Federal Acquisition Regulation Supplement (DFARS), a supplement to the Federal Acquisition Regulation that governs defense contracting.
Inaccurate cybersecurity representations, including an inaccurate score in the Supplier Performance Risk System (SPRS), can create False Claims Act risk.
That's why the self-assessment results and annual affirmation behind an SPRS record, commonly described as CMMC self-attestation, deserve careful review.
The CMMC Compliance Services Available
CMMC compliance services are sold under many names, but the underlying work is consistent. Most engagements for DoD contractors draw from this set:
|
Service |
What It Delivers |
|
Gap assessment |
Where you stand against every applicable requirement, used to identify gaps and prioritize them |
|
Scoping support |
Which systems, people, and providers fall inside your assessment boundary |
|
Remediation and implementation |
The security controls themselves, from access control and data encryption to endpoint protection and logging |
|
Documentation |
The System Security Plan (SSP), policies, procedures, and Plans of Action and Milestones (POA&Ms) |
|
Evidence collection |
Artifacts organized against the requirements they prove |
|
Managed security operations |
Ongoing monitoring, alerting, and incident response run on your behalf |
|
Assessment preparation |
Mock assessments, interview coaching, and evidence review before the real thing |
|
Ongoing compliance management |
Keeping controls, documentation, and scores current between assessment cycles |
A gap assessment alone identifies problems without fixing them, so buying the first item and stopping produces a report rather than a change. Ongoing compliance management is also easy to leave unowned, which is how a compliant environment quietly drifts.
Who Provides CMMC Compliance Support?
Provider categories overlap in marketing but differ in what they can actually do for you. Here's how they separate.
Registered Provider Organizations
A Registered Provider Organization is authorized by the Cyber AB to provide CMMC advisory services, with Registered Practitioners on staff who have completed the required training.
RPOs advise. They interpret requirements, run gap assessments, guide remediation, and prepare you for evaluation. Choosing an RPO is a common entry point for a contractor that wants informed guidance rather than a general IT vendor.
Managed Service Providers and MSSPs
Managed service providers and managed security service providers (MSSPs) implement and operate your security stack. They deploy the technical controls, run the monitoring, and can become the long-term operator.
For many contractors, that's the appeal: handing the security workload to a provider frees the team to stay on core business operations.
Their role comes with a wrinkle worth understanding, though. Depending on what they provide, their services may fall inside your assessment scope, particularly when their systems handle CUI or deliver security functions for the assessed environment.
C3PAOs and Assessors
A CMMC Third-Party Assessment Organization (C3PAO) conducts the formal Level 2 assessment, the CMMC audit most people picture when they think about the program. When those assessments are required, the role carries a strict independence requirement.
The rule is specific: a C3PAO is barred from assessing an organization it has provided CMMC consulting services to within the previous three years. Using your advisor as your assessor inside that window isn't a judgment call, it's a disqualifying conflict.
Compliance Software Platforms
Software can reduce many of the manual hours otherwise spent tracking controls, evidence, and documentation. Purpose-built CMMC compliance software holds requirement status, evidence, and documentation together, and shows readiness without anyone rebuilding a spreadsheet.
For consultants, the same tooling is what makes serving many contractors practical rather than exhausting.
What the 2026 Suspension Changes About CMMC Implementation
On July 13, 2026, the Department of War announced the immediate suspension of CMMC Phase 2 requirements, which had been scheduled to take effect on November 10, 2026, and stood up a CMMC Reform Task Force to review the program.
The change is narrower than the headlines suggested. What's suspended is the Phase 2 implementation that would have made third-party assessment a condition of award.
The CMMC standards themselves are not: department officials described the change as removing the bureaucracy of third-party assessment rather than relaxing the cybersecurity requirements underneath it.
During the review, the Department is enforcing NIST 800-171 Revision 2 through self-assessments and select government-led assessments.
Phase 1 self-assessment obligations remain in force. Where they apply, contractors still conduct self-assessments, submit results to SPRS, complete the required affirmations, and carry False Claims Act risk for inaccurate submissions.
Two dates matter right now. The public comment period closed on August 14, 2026, and the task force is expected to deliver recommendations to the Department CIO around mid-September 2026.
One practical caution during the pause: the clause on your contract is still the clause on your contract until it's modified.
Contracting officers have been instructed to revise ongoing solicitations and eliminate Level 2 C3PAO or Level 3 requirements from current contracts either before the next option period begins or during the next planned administrative modification.
Confirm the status of your specific awards in writing rather than assuming a requirement has already been lifted.
For contractors, the reasonable posture is unchanged. The work of implementing controls, documenting them, and keeping evidence current is the same work whichever verification model returns.
How to Choose CMMC Compliance Support
Your compliance requirements are fixed, and so are the audit requirements written into your contracts. The shape of the help you buy isn't. The market rewards buyers who ask precise questions, and the following five are worth asking every provider.
- Which parts are you actually doing? Advisory, implementation, monitoring, and assessment are different engagements. Get the boundary in writing so nothing falls between providers.
- What CMMC experience do you have? Familiarity with other cybersecurity frameworks is not the same as having taken contractors through CMMC assessments. Ask how many, and at what level.
- Who owns the documentation afterward? An SSP you can't maintain without the consultant is a subscription, not a deliverable.
- How does this continue after the assessment? Ongoing compliance management is where programs succeed or quietly decay. Ask what the second year looks like.
- Can you assess us too? For a Level 2 assessment, the answer has to be no. A C3PAO can't assess an organization it consulted for in the previous three years.
Cost varies enormously with scope, environment size, and how much remediation the gap assessment uncovers. Remediation can easily cost more than the assessment that identified it, so budget separately for the fixes rather than treating the assessment as the full cost.
Where you are in the compliance journey matters too. A contractor with existing regulatory requirements under other frameworks usually starts further along than one facing its first federal obligation.
From CMMC Assessments to Ongoing Compliance Management
One costly mistake in CMMC is treating an assessment as the finish line. It's an ongoing commitment: systems change, staff turn over, and controls drift, which is how a strong score becomes an inaccurate one without anyone deciding to let it happen.
Ongoing compliance management is the discipline that prevents it: continuous monitoring of the controls, evidence collected as work happens rather than reconstructed later, and documentation updated when the environment changes.
Organizations that maintain compliance this way keep their cybersecurity posture and their paperwork describing the same reality.
Keeping objective evidence current can turn assessment preparation from a reconstruction project into a review. Letting it lapse means rebuilding the trail under time pressure.
That's the argument for putting the program somewhere durable rather than in a consultant's project folder.
How MotherBear Supports Your CMMC Compliance Program
Compliance support hours can disappear into work nobody wants to pay for: locating evidence, reconciling documentation against reality, and reconstructing what changed since the last review.
That overhead comes from scattered information, not from the requirements themselves. When requirement status, evidence, and documentation live apart, an engagement can start with an archaeology phase.
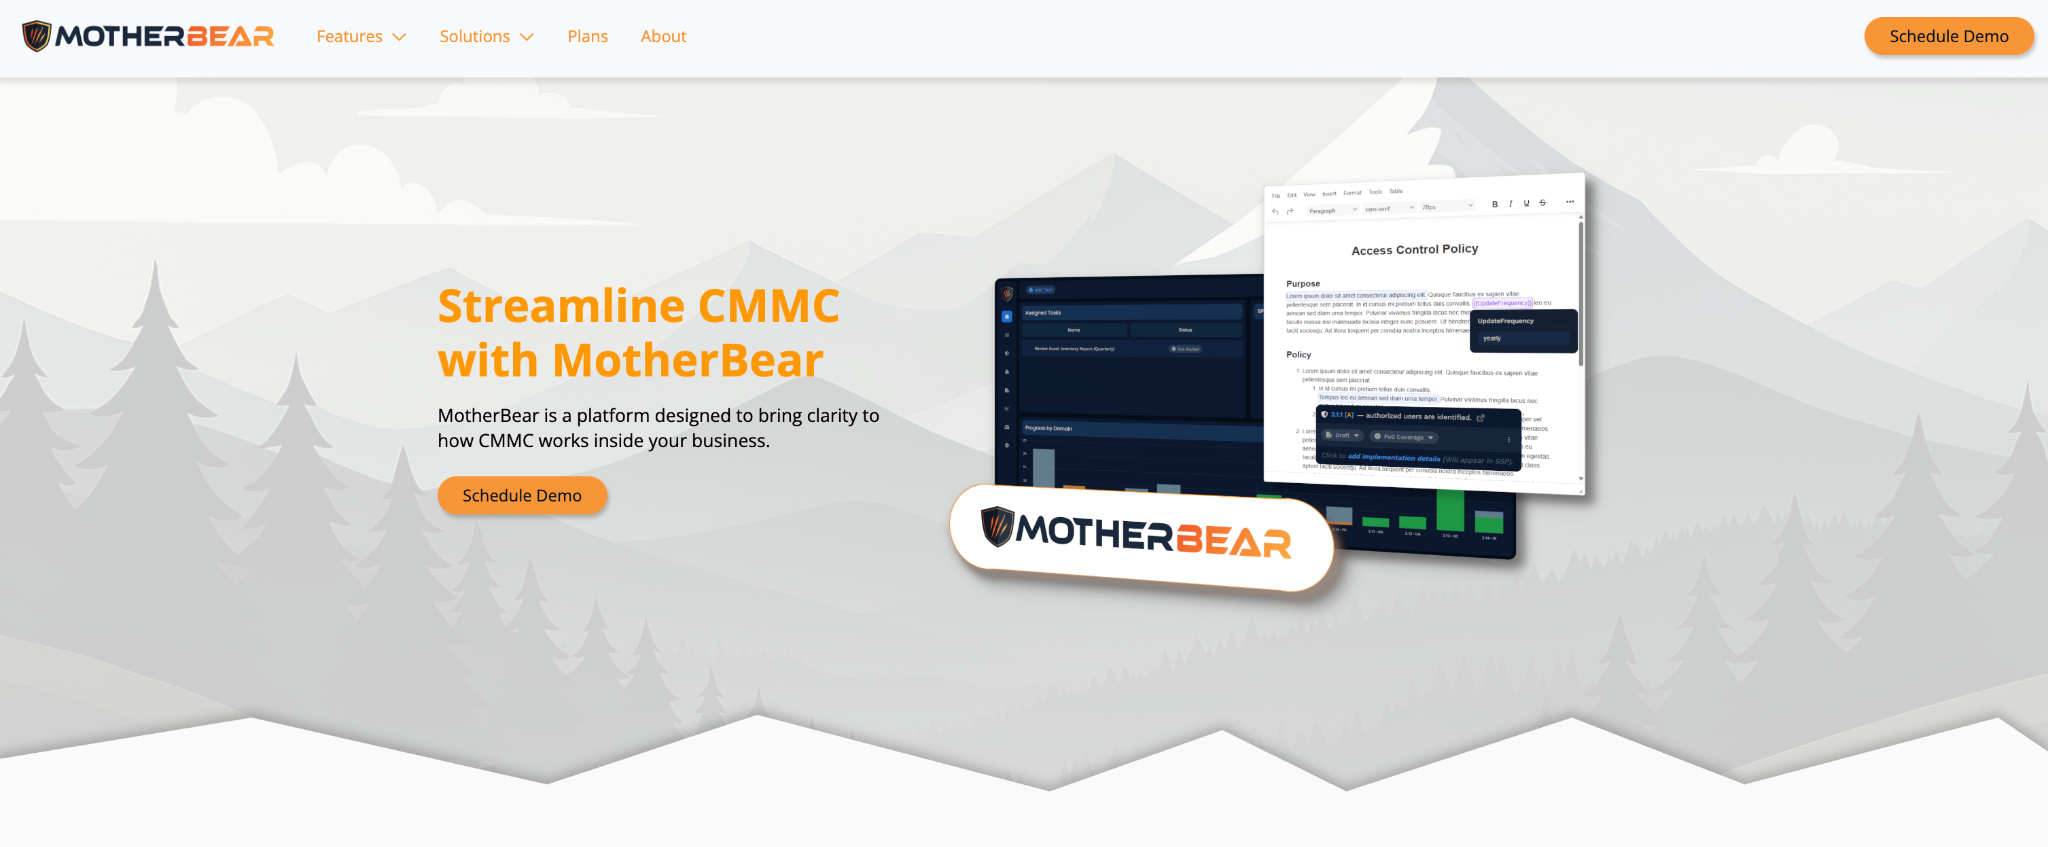
MotherBear gives defense contractors and their consultants a central place to build and store the whole program: requirement status against NIST 800-171, an evidence repository tied to the requirements each artifact proves, SSP and policy materials, remediation work, and assessment readiness in one view.
For consultants and MSPs, separate contractor programs stay organized in the same workspace, with client communication and reporting alongside them. That's what makes supporting multiple contractors a practice rather than a scramble.
The point isn't paperwork for its own sake. It's helping contractors achieve compliance while their security posture and their documentation stay in step.
Book a demo and see how MotherBear turns CMMC compliance support into work you can actually scale.
FAQs About CMMC Compliance Support
Who provides full-service CMMC compliance support?
Registered Provider Organizations, specialized CMMC consultancies, and managed service providers with defense practices all offer end-to-end support, covering gap assessment, remediation, documentation, and ongoing management.
One boundary applies to formal Level 2 certification assessments: a C3PAO can't assess an organization it has provided CMMC consulting to within the previous three years, so recent advisory work rules a firm out as your assessor.
Many contractors combine an advisor for the program with an MSP for operations, which is a reasonable structure as long as responsibilities are documented.
Is NIST 800-171 the same as CMMC?
They're closely linked but not the same thing. At Level 2, NIST 800-171 Revision 2 provides the 110 underlying security requirements for protecting CUI in nonfederal systems, while CMMC defines how implementation is assessed and affirmed.
Level 1 draws its 15 practices from federal acquisition rules rather than NIST 800-171, so the overlap isn't total. In short, one supplies the requirements and the other verifies them.
How much does it cost to be CMMC-compliant?
There's no standard figure, because cost depends mainly on scope rather than headcount alone. The drivers are how much CUI you handle, how your environment is architected, how much of it already meets the requirements, and how much remediation a gap assessment uncovers.
Level 1 is comparatively inexpensive; Level 2 programs involve technical remediation, documentation, tooling, and support hours. Budget separately for remediation rather than treating the assessment fee as the full cost of compliance.
Who is responsible for CMMC compliance?
The contractor is, always. Support providers can implement controls, write documentation, and run monitoring, but the obligation belongs to the company holding the contract, and the affirmation submitted to SPRS is signed by one of its senior officials.
That's why documented responsibility matters when work is shared with an MSP or consultant. Anything you assume a provider is handling, without it being written down, is a gap waiting to surface during an assessment.