---
title: What Is FCI? Federal Contract Information Guide
description: What is FCI? Learn how to identify Federal Contract Information in your business. See how MotherBear can help with CMMC compliance.
image: https://www.motherbearsecurity.com/hubfs/What%20is%20FCI.png
---
[](https://www.motherbearsecurity.com/)
- Features
- [Requirements Tracking Understand how and why you meet requirements](https://www.motherbearsecurity.com/features/requirements-tracking)
- [Documentation Builder Tools to streamline creating Policies, Procedures and your SSP](https://www.motherbearsecurity.com/features/documentation-builder)
- [Evidence Repository Store evidence with ease and ensure you are audit ready](https://www.motherbearsecurity.com/features/evidence-repository)
- [Task Management Assign, track, and manage tasks across your team](https://www.motherbearsecurity.com/features/task-management)
- Solutions
- [For Defense Contractors Purpose built for the Defense Industrial Base](https://www.motherbearsecurity.com/solutions/defense-contractors)
- [For Managed Service Providers Simplify program management for you and your clients](https://www.motherbearsecurity.com/solutions/managed-service-providers)
- [For CMMC Professionals Use tools that help you provide the best value to your clients](https://www.motherbearsecurity.com/solutions/cmmc-professionals)
- [Plans](https://www.motherbearsecurity.com/plans)
- [About](https://www.motherbearsecurity.com/about)
[Schedule Demo](https://www.motherbearsecurity.com/schedule-demo)
# What Is FCI? Federal Contract Information Guide
June 18, 2026

## Table of Contents
1. [TL;DR](https://www.motherbearsecurity.com/blog/what-is-fci#tldr)
2. [What Is FCI?](https://www.motherbearsecurity.com/blog/what-is-fci#What-Is-FCI)
3. [FCI vs. CUI: Key Differences](https://www.motherbearsecurity.com/blog/what-is-fci#FCI-vs-CUI-Key-Differences)
4. [How to Identify FCI in Your Business](https://www.motherbearsecurity.com/blog/what-is-fci#How-to-Identify-FCI-in-Your-Business)
5. [Operational Boundaries for FCI](https://www.motherbearsecurity.com/blog/what-is-fci#Operational-Boundaries-for-FCI)
6. [How to Handle and Protect FCI](https://www.motherbearsecurity.com/blog/what-is-fci#How-to-Handle-and-Protect-FCI)
7. [FCI and CMMC Level 1: What You Need to Know](https://www.motherbearsecurity.com/blog/what-is-fci#FCI-and-CMMC-Level-1-What-You-Need-to-Know)
8. [Manage Your Entire CMMC Program With MotherBear](https://www.motherbearsecurity.com/blog/what-is-fci#Manage-Your-Entire-CMMC-Program-With-MotherBear)
9. [FAQs About What Is FCI](https://www.motherbearsecurity.com/blog/what-is-fci#FAQs-About-What-Is-FCI)
Federal Contract Information (FCI) is non-public information provided by or generated for the federal government under a contract. Some contractors handle it without realizing it.
The records exist in inboxes, shared drives, and project files long before anyone ties them to a compliance program.
FCI sets the scope for [Cybersecurity Maturity Model Certification](https://www.motherbearsecurity.com/blog/what-is-cmmc-compliance) (CMMC) Level 1. The Department of Defense (DoD) began phasing in CMMC on November 10, 2025, and FCI records define which systems fall into your scope. Identifying them early makes assessment prep easier.
This guide explains what FCI is, how to recognize it in your systems, how it differs from [Controlled Unclassified Information](https://www.motherbearsecurity.com/blog/what-is-cui) (CUI), how to handle and protect it, and how CMMC Level 1 ties everything together.
## **TL;DR**
- FCI is non-public information you receive from or create for the government under a contract, including pricing, schedules, project emails, and progress notes. Some teams handle more than they realize.
- An FCI-only environment can self-assess to CMMC Level 1 against 15 Federal Acquisition Regulation (FAR) safeguards and affirm the result annually in the Supplier Performance Risk System (SPRS).
- Where CMMC applies, systems handling CUI generally need Level 2 protection under 110 NIST 800-171 Revision 2 requirements. The contract specifies the required status and assessment type.
- Identifying FCI starts with reviewing each contract's terms and conditions for FAR clause 52.204-21. Then audit private correspondence with agency contacts, primes, and suppliers.
- Protecting FCI means applying 15 basic safeguards to every system that processes, stores, or transmits it, from access control to media disposal.
- [MotherBear](https://www.motherbearsecurity.com/schedule-demo) gives CMMC consultants and defense contractors one place to build and store their entire CMMC program, from the Level 1 baseline that FCI triggers to the 110-control Level 2 program that some contractors need once CUI enters the scope.
## **What Is FCI?**
FCI can originate with either a federal agency or a contractor performing work for it. When these records are provided or created under a government contract to develop or deliver a product or service, and contain information not intended for public release, they qualify as Federal Contract Information.
FCI can include pricing details, delivery schedules, project communications, and similar records that aren't intended for public release.
The duty sits in [FAR clause 52.204-21](https://www.acquisition.gov/far/52.204-21), which requires safeguarding of any covered contractor information system. That is a contractor-owned or contractor-operated system that processes, stores, or transmits FCI, which in practice means non-federal systems such as file shares and email.
The clause calls for 15 basic security practices, and the duty follows the record into whichever system holds it. Contracts that use the revised FAR Part 40 carry the same clause as FAR 52.240-93, so check which numbering your contract uses.
The definition is broad. Because FCI isn't classified and doesn't carry CUI markings, some teams under-protect it. Others overbuild controls for records that only need the FAR baseline.
FCI excludes information the government provides to the public, such as content on government websites, so public pages don't create the same duty. FCI also excludes simple transactional information, such as what is necessary to process payments.
### **Examples of FCI**
FCI can look ordinary. It may not arrive with a label, so pattern recognition beats waiting for a perfect tag.
Look for records like these:
- Award terms, delivery schedules, and pricing details shared after the award.
- Email threads about private instructions, milestones, or issue resolution.
- Progress reports, performance updates, and meeting notes.
- Supplier files and subcontractor deliverables exchanged once work begins.
- Billing notes that reveal non-public contract details (simple payment data is excluded).
Federal contracts create the duty, but daily operations spread the records. A service to the government can produce FCI through a ticket or a status note, and project timelines can qualify when they reveal non-public milestones.
For government contractors, the hard part isn't the definition. It's noticing FCI before it spreads through your company's mailboxes and folders.
## **FCI vs. CUI: Key Differences**
CUI carries stricter markings than FCI. Both sit outside public channels, but the handling burden is different.
| **Area** | **FCI** | **CUI** |
| --- | --- | --- |
| Source | FAR 52.204-21 | 32 CFR Part 2002 and the CUI Registry |
| Sensitivity | Lower category | Sensitive information with formal markings |
| Level impact | Level 1 | Level 2 or higher |
| Markings | No standard marking required | Marked or otherwise identified when required |
| Safeguards | 15 basic FAR safeguards | NIST 800-171 requirements |
CUI covers unclassified information for which laws, regulations, or government-wide policies require or authorize agencies to apply special handling rules. These rules can include safeguarding requirements and dissemination controls.
[Executive Order 13556](https://obamawhitehouse.archives.gov/the-press-office/2010/11/04/executive-order-13556-controlled-unclassified-information) established the program, and the National Archives and Records Administration (NARA) administers it through the CUI Registry. CUI isn't classified, though some categories have national security implications.
Technical drawings can fall on either side of that line. Drawings designated as CUI follow CUI rules, and other drawings tied to the contract may be FCI, so confirm the designation with your contracting officer.
That distinction reshapes your CMMC roadmap. An FCI-only environment is assessed at CMMC Level 1 against 15 basic safeguards through an annual self-assessment.
Once CUI enters the environment, Level 2 applies: 110 NIST 800-171 controls. The contract sets the assessment type, either a self-assessment or a third-party assessment conducted by a CMMC Third-Party Assessment Organization (C3PAO). Preparation time depends on your starting point.
Treat every FCI record as CUI, and the team builds a larger CMMC boundary than needed. Treat CUI as ordinary FCI, and assessors find missing controls.
The clean approach is to settle the[CUI vs FCI](https://www.motherbearsecurity.com/blog/cui-vs-fci) question early, then map each record to its clause, marking, and system owner.
## **How to Identify FCI in Your Business**
Once the definition is clear, identification becomes a review of clauses and workflows, which fits teams that need a practical starting point before a formal assessment.
Work through these actions to understand where FCI lives:
- **Review the contract terms and conditions:** Check each agreement for FAR clause 52.204-21, or 52.240-93 where the revised Part 40 applies.
- **Search private correspondence:** Look through messages with agency contacts, primes, and suppliers.
- **Inventory the tools tied to the work:** List the folders, labels, queues, and collaboration tools your team uses for the contract.
- **Compare outputs to staff files:** Check work statements, outputs, and schedules against the files your staff created.
- **Default unclear records to FCI:** Protect them as FCI until the data owner or contracting officer confirms otherwise, and ask which designation applies if CUI is possible.
That last step prevents a failure pattern in which teams wait for a perfect label and miss unmarked FCI generated for the government.
A simple inventory is less polished than a full map, but it gets contractors moving and keeps the process tied to ownership.
When the inventory outgrows a spreadsheet, dedicated solutions such as MotherBear's [requirements tracking workspace](https://www.motherbearsecurity.com/features/requirements-tracking) give teams one place to connect each record to the requirements and tasks it triggers, from the FAR baseline today to [NIST 800-171](https://www.motherbearsecurity.com/blog/what-is-nist-800-171) once CUI enters the picture.
[*Book a demo now.*](https://www.motherbearsecurity.com/schedule-demo)
## **Operational Boundaries for FCI**
Federal contracts spread private records through finance, program work, and supplier management, and they can reach subcontractors earlier than owners expect. That spread is why FCI deserves a dedicated review before staff assumes a file is harmless.
### **Data and Systems**
Private records can reach help desks soon after kickoff, so systems should be sorted by whether they store FCI.
Systems that only host public content can stay out of scope, while systems that move FCI, including finance tools and archives, need named owners.
That ownership keeps the scope honest. Repeat system reviews after award changes or when suppliers connect, and document any scope change in a process note.
Data maps make ownership visible for individual records as well as the systems that hold them. As a practical tracking method, record the source, owner, and retention needs of each document category.
### **Supplier and Agency Scope**
Subcontractors need the same clarity as internal teams. The clause flows down to applicable subcontracts where systems may store or transmit FCI. A prime contractor may add terms, so defense contractors should confirm each supplier’s obligations.
Anyone who handles FCI, whether an internal team, contractor, or subcontractor, needs a simple intake path and a change log. Government contracts and federal agency messages need the same review, and any public release decisions should be documented.
U.S. government work can include quiet operational files, and sloppy handling at scale can expose non-public contract details. Information security leaders should own the escalation path.
A covered contractor information system can be a modest file share, so security controls should match the way staff uses it. Access control is the first place to look when you secure FCI: define the owner first and let media protection and access decisions follow.
## **How to Handle and Protect FCI**
FAR 52.204-21 lists 15 basic safeguarding requirements, which correspond to a subset of the NIST 800-171 requirements.[FCI compliance](https://www.motherbearsecurity.com/blog/fci-compliance) means implementing each one on every covered system.
These controls give FCI basic protection compared to the heavier expectations on CUI work. Each safeguard still needs to be implemented and demonstrable when a buyer, a prime, or the government asks.
The clearest way to operationalize them is through three habits that the safeguards naturally cluster into. The boundary follows the records, not the org chart.
### **Limit Who Can Reach FCI**
Access control covers who reaches FCI and how their identity gets verified. Start by limiting access to authorized users, and narrow that further to the specific transactions or functions each user needs to do their job.
A contracts coordinator probably doesn't need source code access, and the engineering team probably doesn't need pricing files. From there, authenticate every user, process, and device with unique identifiers before they touch FCI.
Then extend the same discipline to physical access. Lock the rooms where the systems live, escort visitors and monitor their activity, keep physical access logs, and control badges, keys, and other physical access devices.
Some teams trip on the physical side first. A server room that anyone in the office can walk into fails the requirement even when the digital controls are clean.
### **Protect How FCI Moves Through Your Systems**
System protection covers how FCI moves and how the systems that hold it stay clean.
Start at the edges. Verify and control external connections so supplier portals and remote services don't quietly bypass internal boundaries. Watch what gets posted to publicly accessible systems, too, so FCI doesn't end up on a misconfigured share.
Inside that perimeter, monitor communications at the external boundary and at any key internal boundary between subnetworks. Separate publicly accessible system components from internal networks. That separation keeps a public-facing service from pivoting into the FCI environment.
The systems themselves need the same attention. Identify, report, and correct system flaws in a timely manner. Provide malicious code protection at gateways, endpoints, and email, and update those mechanisms when new releases are available.
On top of that, run periodic scans of the environment and real-time scans of any files arriving from external sources.
### **Sanitize Media Before Disposal or Reuse**
A retired laptop or a returned external drive that still holds FCI is an exposure event. Wipe, degauss, or physically destroy any storage that touched FCI before recycling, reissuing to a different team, or sending it back to a vendor.
Document each disposal as you go, following consistent procedures, because that record becomes[CMMC objective evidence](https://www.motherbearsecurity.com/blog/cmmc-objective-evidence) for the annual affirmation later.
The same logic extends to subcontractors. A prime contractor may add flow-down language that subcontractors should confirm before work starts, including how their media gets handled at the end of an engagement. Don't assume suppliers are out of scope.
For teams preparing evidence for all 15 safeguards, MotherBear's [central evidence repository](https://www.motherbearsecurity.com/features/evidence-repository) helps prove proper handling without searching shared drives before an assessment.
## **FCI and CMMC Level 1: What You Need to Know**
For contractors whose DoD contracts require CMMC, Level 1 is the baseline for systems handling only FCI. Phase 1 of the DoD rollout began on November 10, 2025, and it focuses on [Level 1 and Level 2 self-assessment](https://dodcio.defense.gov/cmmc/Resources-Documentation/) requirements.
On July 13, 2026, the Department of War (DoW), the secondary name for the Department of Defense, suspended Phase 2 and the remaining rollout milestones pending a task force review.
During the suspension, only Level 1 (Self) and Level 2 (Self) can be designated in new solicitations, and Phase 1 obligations continue.
Level 1 was always a self-assessment, so the suspension doesn't change what a Level 1 contractor owes. Check the DoD CIO's CMMC page for the review's outcome before you plan around any Phase 2 date.
That doesn't make self-assessment a paperwork shortcut. Contractors still need cybersecurity practices they can explain and repeat, and an Affirming Official completes the annual[CMMC self-attestation](https://www.motherbearsecurity.com/blog/cmmc-self-attestation) through SPRS.
Level 2 changes the evidence burden and can be verified by self-assessment or third-party assessment, depending on the contract, while Level 3 applies to selected programs and sits outside Phase 1.
Solicitations name the required level and assessment type through Defense Federal Acquisition Regulation Supplement (DFARS) clause 252.204-7025.
That requirement depends on whether the work involves FCI or CUI, and the[DFARS vs CMMC](https://www.motherbearsecurity.com/blog/dfars-vs-cmmc) clause map explains how the 2026 renumbering affects those references.
CMMC Level 1 covers 15 security requirements, drawn directly from FAR 52.204-21.
Suppliers whose contracts require Level 1 follow the self-assessment process from scoping through annual affirmation. If CUI later enters the work, the applicable[CMMC levels](https://www.motherbearsecurity.com/blog/cmmc-levels) and assessment requirements may change.
Weak evidence is a real risk. A contractor that knowingly affirms a status it can't support can face False Claims Act liability, and named owners for each practice make the evidence easier to produce and defend.
## **Manage Your Entire CMMC Program With MotherBear**
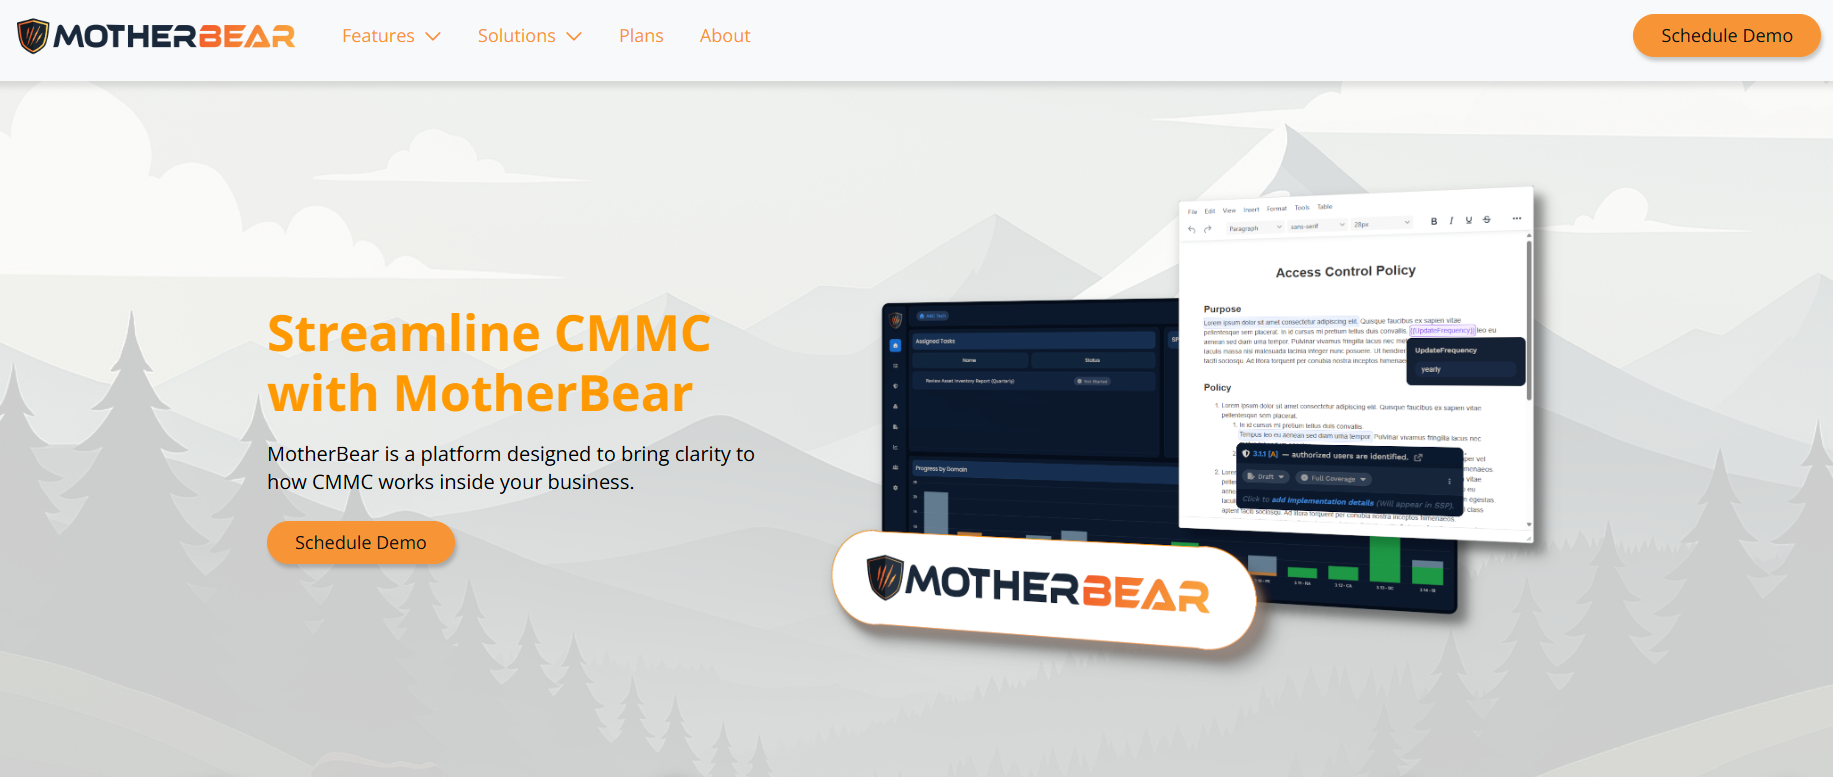
Some defense contractors don't stay FCI-only. The first contract that brings CUI in moves the program from 15 FAR safeguards to 110 NIST 800-171 controls, with a self-assessment or third-party assessment depending on the contract.
Teams can get caught flat-footed when evidence still lives in shared drives and email threads. [MotherBear](https://www.motherbearsecurity.com/) gives CMMC consultants and defense contractors one workspace to build and store the entire program.
Track requirements for Level 1 and Level 2, organize evidence, manage documentation, and keep tasks moving before assessment. Consulting firms run multiple client programs from one view; contractors keep their own program tied to the records that define its scope.
[***Book a demo and see how MotherBear turns scattered FCI and CUI records into a CMMC program you can actually run.***](https://www.motherbearsecurity.com/schedule-demo)
## **FAQs About What Is FCI**
### **What does FCI stand for?**
FCI stands for Federal Contract Information. It is non-public information that the government provides to a contractor, or that a contractor generates for the government, under a contract.
The definition appears in FAR clause 52.204-21 and covers work to develop or deliver a product or service. It excludes information the government provides to the public and simple transactional data used to process payments.
### **What is the definition of Federal Contract Information according to the FAR?**
Federal Contract Information is non-public information provided by or generated for the government under a federal contract to develop or deliver a product or service.
It excludes information provided on public websites and simple transactional information needed to process payments. The definition appears in FAR clause 52.204-21, or 52.240-93 under the applicable FAR overhaul deviation.
### **Is FCI the same as CUI?**
No. FCI is lower-sensitivity information covered by basic safeguards under FAR 52.204-21.
Controlled Unclassified Information (CUI) requires stronger controls and formal handling rules under 32 CFR Part 2002 and triggers CMMC Level 2 instead of Level 1, so the distinction affects scope, assessment type, and timeline.
### **Which CMMC level applies to FCI?**
Where a DoD contract requires CMMC and involves only FCI, Level 1 applies. Contractors complete an annual self-assessment against 15 requirements and submit results and an affirmation in SPRS.
If the work involves CUI, check the contract for the required level and assessment type.
## Need CMMC Level 1?
Book a demo of MotherBear to see how you can simplify CMMC
[Schedule Demo](https://www.motherbearsecurity.com/schedule-demo)
## Read On
[](https://www.motherbearsecurity.com/blog/cmmc-for-defense-contractors)
### [CMMC for Defense Contractors: 2026 Compliance Guide](https://www.motherbearsecurity.com/blog/cmmc-for-defense-contractors)
Winning defense contracts increasingly depends on more than technical capabilities, pricing, and...
[](https://www.motherbearsecurity.com/blog/what-is-nist-800-171)
### [What Is NIST 800-171? A Brief 2026 Guide](https://www.motherbearsecurity.com/blog/what-is-nist-800-171)
What is NIST 800-171, and why does a single contract clause suddenly hinge on it? That’s what most...
[](https://www.motherbearsecurity.com/blog/google-workspace-cmmc-compliance)
### [Google Workspace CMMC Compliance: What’s Actually Required](https://www.motherbearsecurity.com/blog/google-workspace-cmmc-compliance)
For years, defense contractors running Google Workspace were pushed toward Microsoft GCC High...

#### Pages
[Home](https://www.motherbearsecurity.com)
[Plans](https://www.motherbearsecurity.com/plans)
[About](https://www.motherbearsecurity.com/about)
[Blog](https://www.motherbearsecurity.com/blog)
#### Features
[Requirements Tracking](https://www.motherbearsecurity.com/features/requirements-tracking)
[Documentation Builder](https://www.motherbearsecurity.com/features/documentation-builder)
[Evidence Repository](https://www.motherbearsecurity.com/features/evidence-repository)
[Task Management](https://www.motherbearsecurity.com/features/task-management)
#### Solutions
[For Defense Contractors](https://www.motherbearsecurity.com/solutions/defense-contractors)
[For Managed Service Providers](https://www.motherbearsecurity.com/solutions/managed-service-providers)
[For CMMC Professionals](https://www.motherbearsecurity.com/solutions/cmmc-professionals)
---
© 2026 Mother Bear Security, Inc. All rights reserved.
Privacy Policy
```json
{
"@context" : "https://schema.org",
"@type" : "BlogPosting",
"author" : {
"@type" : "Person",
"name" : "Nick Marteney",
"url" : "https://www.motherbearsecurity.com/blog/author/nick-marteney"
},
"dateModified" : "2026-10-30T11:45:54.099Z",
"datePublished" : "2026-06-18T11:26:59.000Z",
"headline" : "What Is FCI? Federal Contract Information Guide",
"image" : [ "https://www.motherbearsecurity.com/hubfs/What%20is%20FCI.png" ],
"mainEntityOfPage" : {
"@id" : "https://www.motherbearsecurity.com/blog/what-is-fci",
"@type" : "WebPage"
},
"publisher" : {
"@type" : "Organization",
"logo" : {
"@type" : "ImageObject",
"url" : "https://www.motherbearsecurity.com/hubfs/mbs-logo-transparent-h128.png"
},
"name" : "Mother Bear Security"
}
}
```