Table of Contents
CMMC stands for Cybersecurity Maturity Model Certification, and most guidance on it explains what work has to happen. Far less explains who does it.
That gap shows up predictably. A contractor finishes a gap assessment, produces a solid remediation list, and then the program slows because the person nominally running it has a full-time job doing something else.
For Department of Defense (DoD) contractors in the Defense Industrial Base (DIB), managing a CMMC program is a staffing and governance problem before it's a technical one, whatever the DoD contract requires.
Someone has to own the program, someone has to own each control, someone has to sign the affirmation, and someone has to decide what happens when those people disagree.
This guide covers the roles, the meeting cadence that keeps a program current, and how to report on it in the two directions that matter.
TL;DR
- A workable CMMC program benefits from a named program owner and control owners, while the Affirming Official is the formal role responsible for affirming continuing compliance.
- The Affirming Official carries legal and contractual responsibility for continuing compliance, while knowingly false cybersecurity representations can create False Claims Act exposure.
- Governance cadence matters more than tooling. A practical model uses a short monthly review, a quarterly evidence check, and the required annual affirmation cycle.
- Report upward on compliance investment and risk, and outward to prime contractors on status. Those are different conversations with different evidence.
- MotherBear gives program owners one place to see requirement status, owners, evidence, and open work, so the management layer runs on facts rather than recollection.
What Managing a CMMC Program Involves Under the CMMC Framework
Program management sits above implementation. The technical work is building controls; the management work is making sure the right people own them, that the work keeps happening, and that the organization can answer questions about its own state.
Like most cybersecurity frameworks, CMMC defines the security requirements, assessment process, scoping rules, and affirmation responsibilities. It does not prescribe a program owner, control-owner matrix, or meeting cadence.
The structure below is a practical governance model for keeping that work accountable. The cybersecurity requirements are published; the compliance requirements around who runs them are not.
For smaller defense contractors, that's often the harder half. There's rarely a compliance department, so the program runs on borrowed time from people hired to do something else.
Getting the role structure right is what makes that workable.
Who Owns What: Mapping CMMC Requirements to People
Ownership has to reach individuals. A requirement owned by "IT" is owned by nobody in particular once several people could plausibly have handled it.
The Program Owner
One person should be accountable for the program as a whole: scope decisions, the remediation plan, the evidence position, and whether the organization can demonstrate compliance on request.
That person owns the reported security posture and the organization's cybersecurity posture as leadership understands it, even though they rarely control every system behind it.
This isn't necessarily a security role. It's often an operations lead, a quality manager, or whoever already coordinates work between departments, because most of the job is chasing people rather than configuring systems.
The role needs authority. A program owner who can't get time from IT or a decision from leadership will produce accurate status reports about a program that isn't moving.
Control Owners for Access Control and Configuration Management
In this governance model, each requirement family should have someone accountable for the controls inside it and for the evidence proving they work.
- Access control: Usually IT or the systems administrator, covering account management, least privilege, and access reviews.
- Configuration management: Whoever sets baselines and approves changes, since this family fails quietly when change processes drift.
- Media protection and physical protection: Often facilities or operations rather than IT, since physical access records and media handling sit outside the server room.
- Personnel security: Typically HR, covering personnel screening and security-related steps during transfers and terminations.
- Awareness and training: Whoever coordinates security training, including role-based training and training records.
- Incident response: Needs a named decision-maker, not just an incident response plan in a folder.
Communications Protection and Technical Control Owners
System and communications protection, audit logging, and system and information integrity usually sit with the same technical owner, along with the monitoring tools behind those security controls. That concentration is worth watching.
When one administrator owns a third of the control set, the program has a single point of failure. That's manageable while they're present and expensive when they leave.
The mitigation doesn't have to be another hire. It can be documentation detailed enough for a successor to follow, with evidence that remains understandable when ownership changes.
The Affirming Official
This role deserves its own consideration, because it carries exposure the others don't.
The Affirming Official is the senior-level representative responsible for making sure the organization meets CMMC Program requirements and has the authority to affirm continuing compliance in the Supplier Performance Risk System (SPRS).
The Affirming Official must provide annual compliance affirmations after a Final CMMC Status, with additional affirmations required when Conditional or Final status is achieved and after POA&M closeout, where applicable.
The role carries legal and contractual responsibility for continuing compliance. Knowingly false cybersecurity representations can also create False Claims Act exposure.
Two practical consequences follow:
- The person signing should understand what they're signing rather than approving a summary someone handed them.
- They need a reliable way to verify the position before each affirmation, which is a program management responsibility rather than a personal one.
An Affirming Official who asks hard questions before signing is doing the job correctly.
When One Person Holds Several Roles
In smaller organizations, the program owner, the main control owner, and the Affirming Official may be two people or even one.
That's workable, and pretending otherwise doesn't help anyone. What matters is acknowledging the concentration rather than obscuring it.
Three safeguards help:
- Write down who holds which role even when the list is short, because turnover happens and accountability has to survive absences.
- Build in a second reviewer for the affirmation, even informally.
- Document to a standard a stranger could follow, because the person holding three roles is the person whose absence stops everything.
Governance Cadence for CMMC Compliance
Programs don't fail at the plan. They fail in month four, when nothing forces a check-in, and the work quietly stops.
A cadence fixes that more reliably than any tool. A practical cadence for a smaller CMMC program has three rhythms:
- Monthly, 30 minutes: Review open remediation items, blocked work, and anything that changed in the environment. Short and boring is the goal.
- Quarterly, longer: Walk the evidence position and whatever continuous monitoring has surfaced. Which requirements have current proof, which have aging artifacts, and which have none.
- Annually: The affirmation cycle, plus a review of scope against contracts won or lost during the year.
Add one trigger-based review. Any significant change to the environment gets checked against the assessment scope before implementation rather than discovered afterward.
That's the whole governance model, and it's what continuous compliance looks like in a small organization.
Teams that keep this cadence make annual compliance affirmations and required reassessments routine; teams that don't often end up rebuilding their evidence position when the next compliance event arrives.
A periodic risk assessment feeds the same cycle, since it tells you which open items actually matter.
Reporting Before and After a CMMC Assessment
Program management involves two audiences who want different things, and conflating them produces reports that satisfy neither.
Reporting Upward on Compliance Investment
Leadership wants to know what the program costs, what risk it retains, and whether contract eligibility is secure.
Useful upward reporting is short: requirements met versus open, remediation items past their target date, the spend needed to achieve compliance against the plan, and any contract exposure created by open gaps.
Leadership rarely needs control-level detail. A board-level view that lists individual requirements buries the decision they actually have to make, which is usually about funding or priority.
Reporting Outward to Prime Contractors
Prime contractors throughout the defense sector want to know whether you're a risk in the defense supply chain.
That conversation runs on status and dates rather than on your internal remediation plan, and it's becoming routine throughout the DoD supply chain as the defense industry adjusts.
Keep a short, current position you can share: your CMMC level, your assessment type, your status and date, and your affirmation currency. Primes increasingly ask before award, and a contractor who can answer in one email is easier to work with than one who needs two weeks.
Don't overshare. A formal Plan of Action and Milestones (POA&M) is part of the assessment and remediation record when Conditional status is used, not something you should automatically disclose to a prime contractor.
CMMC Audit Prep: How the Program Owner Coordinates a Certified Assessor Visit
"CMMC audit" is common shorthand, but the program formally uses the term assessment. From a program-management perspective, preparation is mainly about logistics, ownership, and traceability rather than a last-minute technical sprint.
Before an initial assessment, the program owner focuses on logistics and traceability:
- Confirming evidence is current and retrievable
- Making sure the System Security Plan (SSP) matches the environment
- Making sure control owners are available and know their own controls
- Resolving scope questions before anyone else raises them
The audit process moves faster when evidence maps to assessment objectives rather than to control numbers alone, which is also what a security assessment tests.
Where a certified assessor is involved, independence rules matter.
A CMMC Ecosystem member that served as a consultant preparing the organization for a CMMC assessment within the previous three years cannot participate in that Level 2 certification assessment, which affects who you hire for readiness work.
One current note: CMMC Phase II was suspended in July 2026. During the suspension, new requirements may designate Level 1 (Self) or Level 2 (Self), while voluntary Level 2 third-party certification assessments through C3PAOs remain available.
If a third-party assessment returns as a condition of award, the certification level a contract specifies will shape how much governance the program needs.
For Level 2, the management work still matters because the self-assessment evaluates the same 110 NIST 800-171 Revision 2 security requirements.
Matching Management Effort to Your CMMC Level
Not every program needs the same structure, and over-building the management layer wastes the capacity you need for the actual work.
A Level 1 program handling only Federal Contract Information (FCI) can usually run with one owner, an annual self-assessment cycle, and a simple evidence folder structure. The 15 basic safeguarding requirements represent basic cyber hygiene, but they do not require a separate governance committee.
A Level 2 program handling Controlled Unclassified Information (CUI) needs the full structure: named control owners, a real cadence, and evidence discipline, because 110 requirements and their assessment objectives exceed what one person can track by memory.
Cybersecurity practices that protect Controlled Unclassified Information have to be maintained continuously, and teams that maintain CMMC compliance year-round can reduce the rework and disruption that comes with rebuilding before each cycle.
Level 3 supports the Department's most critical programs and technologies, the highest priority programs in the portfolio, and may justify more dedicated staffing because it adds enhanced security requirements and government-led assessment.
Those programs address advanced persistent threats and sensitive data with national security implications.
Not all controls carry the same management weight either, so concentrate governance attention where evidence is hardest to keep current.
Match the management overhead to the CMMC level your contracts actually require, not to the most demanding scenario you can imagine.
Manage Your CMMC Program Easily With MotherBear
The management layer runs on one question: what is the current state, and who owns the parts that aren't done?
Answering it is hard when requirement status sits in a spreadsheet, evidence sits in a drive, and ownership lives in someone's memory. The program owner ends up assembling a picture rather than reading one.
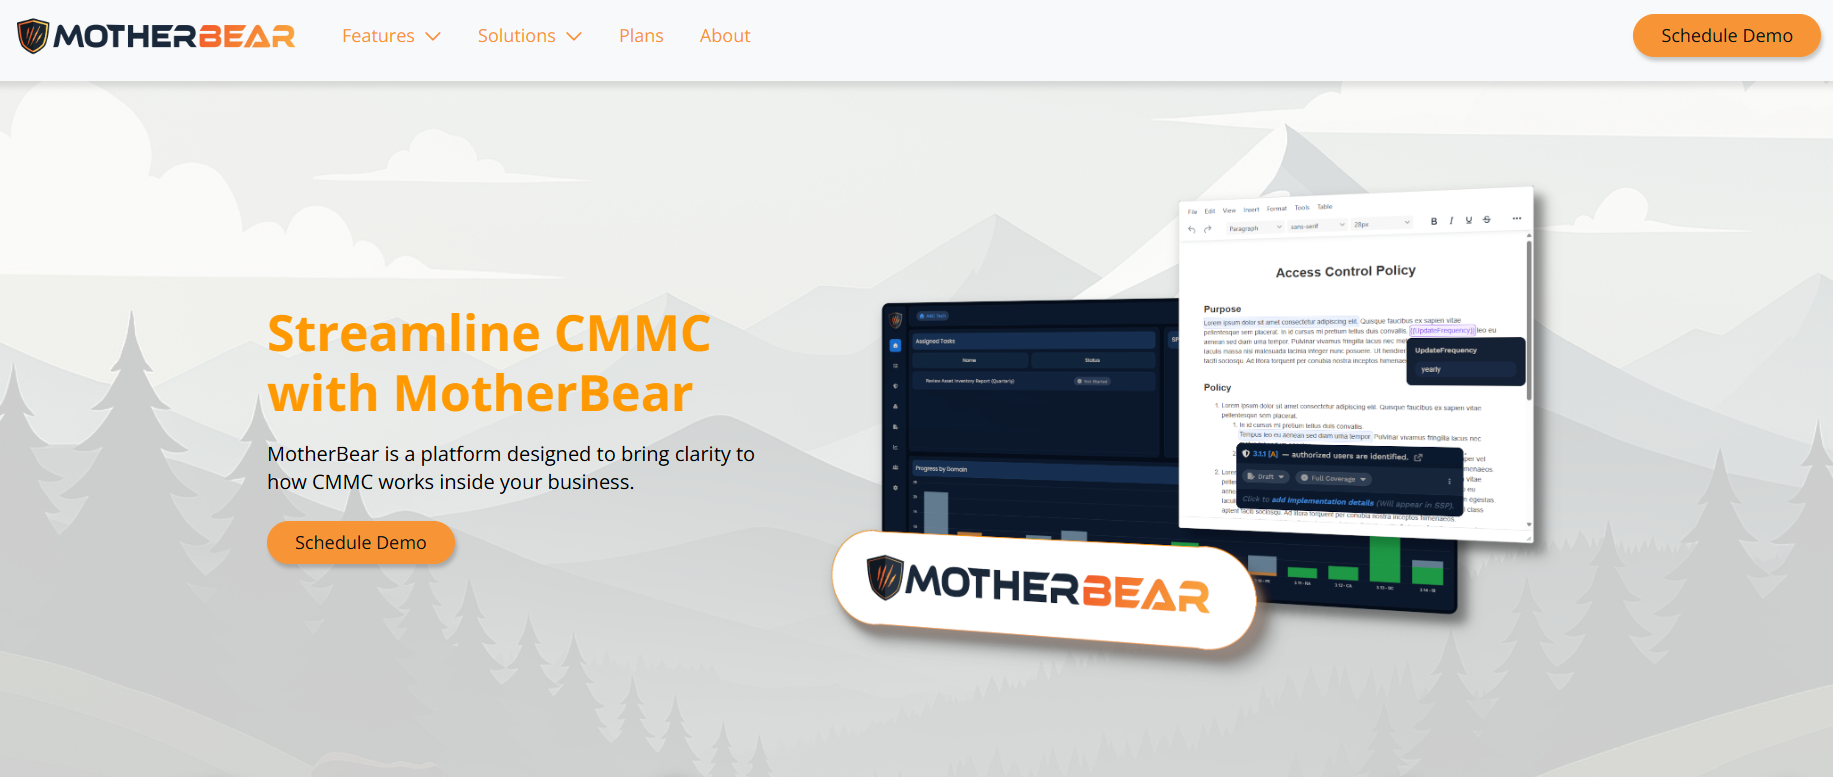
MotherBear gives defense contractors and their consultants one workspace for the whole picture.
Requirement status against the National Institute of Standards and Technology (NIST) standard 800-171, the CMMC evidence behind each requirement, documentation, and management tasks with named owners and deadlines all sit together.
For a program owner, that turns the monthly review into a readout. For consultants managing several contractor programs, it means every client program has the same structure rather than depending on who set it up.
Book a demo and see how MotherBear keeps the management layer current.
FAQs About How to Manage a CMMC Program
Is CMMC compliance difficult?
The difficulty is sustained coordination rather than technical complexity. Most requirements are ordinary security practice, but implementing them, documenting each one, evidencing them, and keeping that current while the business changes is a long project.
Organizations with an existing security program find it manageable. Those starting from informal practices usually find the documentation and ownership work harder than the technology.
What are the best software solutions to simplify CMMC compliance?
The right platform depends on how many frameworks you carry. Organizations managing several compliance programs benefit from broad governance tools, while contractors focused on CMMC generally move faster with a purpose-built option.
For program management specifically, what matters is whether requirement status, evidence, and ownership stay connected. A platform that shows current state without assembly is worth more than one with a longer feature list.
Can you self-certify CMMC?
You can self-assess, which is the current path for Level 1 and Level 2 while Phase 2 is suspended. Your organization conducts the assessment, records the result in SPRS, and the Affirming Official affirms it.
That affirmation is a formal representation to the government rather than an internal sign-off, so the evidence behind it should hold up to the standard an outside assessor would apply.
How much do CMMC professionals make?
Pay varies widely because "CMMC professional" covers program managers, compliance analysts, consultants, and assessors. In a September 2026 snapshot of open CMMC-focused roles with published salary ranges, the median advertised midpoint was about $139,000, with the middle half ranging from roughly $115,000 to $179,000.
Treat that as a snapshot of advertised roles rather than a fixed CMMC salary benchmark. Depending on the role, employers may prefer or require CMMC ecosystem credentials such as CCP or CCA.