---
title: "How to Choose a CMMC Provider: A Buyer's Checklist"
description: Learn how to choose a CMMC provider effectively. Discover how MotherBear can help you manage your CMMC compliance with ease.
image: https://www.motherbearsecurity.com/hubfs/How%20to%20choose%20a%20CMMC%20provider.png
---
[](https://www.motherbearsecurity.com/)
- Features
- [Requirements Tracking Understand how and why you meet requirements](https://www.motherbearsecurity.com/features/requirements-tracking)
- [Documentation Builder Tools to streamline creating Policies, Procedures and your SSP](https://www.motherbearsecurity.com/features/documentation-builder)
- [Evidence Repository Store evidence with ease and ensure you are audit ready](https://www.motherbearsecurity.com/features/evidence-repository)
- [Task Management Assign, track, and manage tasks across your team](https://www.motherbearsecurity.com/features/task-management)
- Solutions
- [For Defense Contractors Purpose built for the Defense Industrial Base](https://www.motherbearsecurity.com/solutions/defense-contractors)
- [For Managed Service Providers Simplify program management for you and your clients](https://www.motherbearsecurity.com/solutions/managed-service-providers)
- [For CMMC Professionals Use tools that help you provide the best value to your clients](https://www.motherbearsecurity.com/solutions/cmmc-professionals)
- [Plans](https://www.motherbearsecurity.com/plans)
- [About](https://www.motherbearsecurity.com/about)
[Schedule Demo](https://www.motherbearsecurity.com/schedule-demo)
# How to Choose a CMMC Provider: A Buyer's Checklist
October 30, 2026

## Table of Contents
1. [TL;DR](https://www.motherbearsecurity.com/blog/how-to-choose-a-cmmc-provider#tldr)
2. [Who Does What in the CMMC Ecosystem](https://www.motherbearsecurity.com/blog/how-to-choose-a-cmmc-provider#Who-Does-What)
3. [Signals That Should Take a Provider Off Your List](https://www.motherbearsecurity.com/blog/how-to-choose-a-cmmc-provider#Signals)
4. [8 Questions to Ask on the First Call](https://www.motherbearsecurity.com/blog/how-to-choose-a-cmmc-provider#Questions)
5. [What Happens When the Relationship Ends](https://www.motherbearsecurity.com/blog/how-to-choose-a-cmmc-provider#What-Happens)
6. [Matching CMMC 2.0 Levels to What Defense Contractors Need](https://www.motherbearsecurity.com/blog/how-to-choose-a-cmmc-provider#Matching-CMMC)
7. [From Full Compliance to Competitive Advantage](https://www.motherbearsecurity.com/blog/how-to-choose-a-cmmc-provider#Full-Compliance)
8. [How MotherBear Keeps Your CMMC Compliance Program Yours](https://www.motherbearsecurity.com/blog/how-to-choose-a-cmmc-provider#How-MotherBear)
9. [FAQs About How to Choose a CMMC Provider](https://www.motherbearsecurity.com/blog/how-to-choose-a-cmmc-provider#FAQs)
Three proposals land on your desk, and all of them use the same buzzwords: [Cybersecurity Maturity Model Certification](https://www.motherbearsecurity.com/blog/what-is-cmmc-compliance) (CMMC) expertise, defense experience, assessment support, ongoing compliance.
Separating the firms that have done this from the ones that added the vocabulary in 2025 takes about 20 minutes, provided you know which registries to check and which questions produce answers nobody can rehearse.
This guide explores how to choose the best CMMC provider.
## **TL;DR**
- The provider labels come from different systems and overlap. One firm can be an advisory organization, your IT operator, and inside your assessment scope all at once.
- Two checks eliminate weak candidates fast: verifying any Cyber AB designation they claim, and asking how they'd evidence the requirements assigned to them where they touch [Controlled Unclassified Information](https://www.motherbearsecurity.com/blog/what-is-cui) (CUI).
- Documentation depth is the sharpest test available, because Level 2 is assessed at a finer grain than most providers write to.
- Ask what you keep when the engagement ends. That answer decides whether changing providers costs you a few weeks or your entire compliance record.
- [MotherBear](https://www.motherbearsecurity.com/schedule-demo) holds requirement status, evidence, and documentation in a workspace your organization owns, so a change of provider doesn't take the program with it.
## **Who Does What in the CMMC Ecosystem**
The labels in this market come from different places, which is why they get used interchangeably in sales conversations. A certified third-party assessment organization (C3PAO) and external service provider (ESP) are defined in the Department of Defense (DoD) regulation at [32 CFR Part 170](https://www.ecfr.gov/current/title-32/subtitle-A/chapter-I/subchapter-G/part-170).
A [Registered Practitioner Organization](https://www.motherbearsecurity.com/blog/cmmc-rpo) (RPO) is a Cyber AB designation. [Managed service provider](https://www.motherbearsecurity.com/blog/cmmc-for-msps) (MSP) describes a business model, not a credential.
They also overlap: within the CMMC program's ecosystem, an RPO can be an MSP. Sorting out which hat a firm is wearing saves smaller firms in the Defense Industrial Base (DIB) real procurement time.
### **MSPs and Managed Security Service Providers**
An MSP runs IT operations. A managed security service provider (MSSP) runs monitoring, access control, multi-factor authentication, software updates, intrusion detection systems, and response to cyber incidents.
Be clear about which functions each one is responsible for before you sign, because gaps between them land on your assessment record.
Many contractors need both, and neither role automatically brings CMMC depth or knowledge of current cybersecurity standards for defense work.
### **RPOs and CMMC Requirements Expertise**
An RPO is registered with the Cyber AB for advisory and implementation work and must employ at least one Registered Practitioner for gap assessments, documentation, remediation guidance, and mock assessments.
An RPO can absolutely assess your [CMMC readiness](https://www.motherbearsecurity.com/blog/cmmc-readiness). What the designation doesn't authorize is the official Level 2 certification assessment or issuing a certificate.
### **C3PAOs and Your Certification Level**
A certified third-party assessment organization conducts the Level 2 certification assessment where that path applies, with certified assessors working under it. Those requirements are suspended at present, so this matters for planning rather than for a current procurement.
One rule holds regardless: a C3PAO cannot assess an organization it consulted for within the previous three years.
### **External Service Providers and Assessment Scope**
An IT or cybersecurity service provider whose assets process, store, or transmit CUI or Security Protection Data can become an external service provider for CMMC purposes, and the treatment then splits. Services from a non-cloud provider are assessed within your own assessment scope.
A cloud service provider handling CUI instead has to meet security requirements equivalent to the Federal Risk and Authorization Management Program (FedRAMP) Moderate baseline under Defense Federal Acquisition Regulation Supplement (DFARS) clause [252.204-7012](https://www.acquisition.gov/dfars/252.204-7012-safeguarding-covered-defense-information-and-cyber-incident-reporting.).
That makes the practical question narrow. A provider that can secure CUI in your environment, and protect CUI under assessment, matters more than one with the longest service list.
Under the full program, readiness and certification come from different firms. Right now that's academic for most buyers: with Phase 2 suspended, only [Level 1 (Self) and Level 2 (Self)](https://www.motherbearsecurity.com/blog/cmmc-level-1-vs-level-2) can be designated, so the assessment you owe is one you conduct yourself.
### **Signals That Should Take a Provider Off Your List**
Some answers mean walk away rather than negotiate.
- **A claimed credential they can't back up:** RPO and C3PAO designations are published and searchable in the Cyber AB Marketplace. An ordinary MSP doesn't need one, but a firm claiming a Cyber AB designation that isn't listed has a problem worth taking seriously.
- **They can't say how they'd evidence their part:** A firm that handles CUI on your behalf should be able to explain how it satisfies and documents the requirements assigned to it. Not every provider needs its own status, but every provider needs that answer.
- **Responsibility splits live in nobody's document:** Assessors examine provider processes and may interview their staff. Without a customer responsibility matrix or equivalent shared responsibility matrix, the ambiguity becomes your finding, not theirs.
- **Their readiness work stops at 110:** Level 2 is evaluated through 320 assessment objectives, and that's where assessors make findings. A firm that can't map implementation and evidence down to the applicable objectives is preparing you one layer above the assessment, whatever the System Security Plan (SSP) says.
- **Nobody they've worked with has finished:** A quote on a website is marketing. Ask to speak with a contractor who went the whole distance with them and came out the other side.
- **They're gone by assessment day:** Some firms deliver a documentation package and step back, which leaves your team explaining systems somebody else configured.
- **The quote assumes nothing breaks:** Readiness pricing that excludes remediation is common, and so are promises about outcomes nobody can control. Ask what the invoice looks like when the gap assessment turns up 40 open items.
## **8 Questions to Ask on the First Call**
These questions determine whether you're buying expertise or vocabulary. A provider's ability to answer them specifically, without retreating into generalities, tells you most of what you need.
1. If your services enter our CMMC scope, how will you satisfy and evidence the requirements assigned to you?
2. If you claim a Cyber AB designation or a certification status of your own, where do we verify it?
3. Can you show a shared responsibility matrix mapping your services to the National Institute of Standards and Technology (NIST) standard 800-171?
4. At what level do you write documentation: control or assessment objective?
5. Can you connect us with clients who completed a [CMMC assessment](https://www.motherbearsecurity.com/blog/cmmc-assessment-guide) after working with you?
6. What does your support look like during the assessment itself?
7. What does compliance management look like in year two, and does it run on internal tools we can access?
8. How would you approach scoping our specific requirements and data flows?
The tell is where they begin. A firm that opens with your data flows rather than a standard package has done this before.
## **How to Identify FCI in Your Business**
Once the definition is clear, identification becomes a review of clauses and workflows, which fits teams that need a practical starting point before a formal assessment.
Work through these actions to understand where FCI lives:
- **Review the contract terms and conditions:** Check each agreement for FAR clause 52.204-21, or 52.240-93 where the revised Part 40 applies.
- **Search private correspondence:** Look through messages with agency contacts, primes, and suppliers.
- **Inventory the tools tied to the work:** List the folders, labels, queues, and collaboration tools your team uses for the contract.
- **Compare outputs to staff files:** Check work statements, outputs, and schedules against the files your staff created.
- **Default unclear records to FCI:** Protect them as FCI until the data owner or contracting officer confirms otherwise, and ask which designation applies if CUI is possible.
That last step prevents a failure pattern in which teams wait for a perfect label and miss unmarked FCI generated for the government.
A simple inventory is less polished than a full map, but it gets contractors moving and keeps the process tied to ownership.
When the inventory outgrows a spreadsheet, dedicated solutions such as MotherBear's [requirements tracking workspace](https://www.motherbearsecurity.com/features/requirements-tracking) give teams one place to connect each record to the requirements and tasks it triggers, from the FAR baseline today to [NIST 800-171](https://www.motherbearsecurity.com/blog/what-is-nist-800-171) once CUI enters the picture.
[*Book a demo now.*](https://www.motherbearsecurity.com/schedule-demo)
## **What Happens When the Relationship Ends**
Providers get acquired, lose the staff who knew your environment, or stop fitting your business. When that happens, companies that own their documentation switch vendors in weeks. The ones that don't start over.
- **Who owns the documentation?** Your SSP and policies should be yours in editable form, not locked in a provider's template system or delivered as flattened files you can't maintain.
- **Where does the evidence live?** If artifacts sit in the provider's platform under their account, your compliance record leaves with them.
- **Is the control data portable?** Requirement status, remediation history, and assessment records represent years of work. Ask exactly how you'd export it.
- **What's the offboarding process?** A provider who has thought about this has an answer. One who hasn't will improvise at the worst moment.
Good providers answer these easily, because their value is expertise rather than holding your data.
## **Matching CMMC 2.0 Levels to What Defense Contractors Need**
Under CMMC 2.0, the [CMMC level](https://www.motherbearsecurity.com/blog/cmmc-levels) your contracts require should shape the engagement.
### **Level 1: Confirm the CMMC Level Before You Buy**
Defense contractors handling only [Federal Contract Information](https://www.motherbearsecurity.com/blog/what-is-fci) (FCI) face 15 requirements and a self-assessment. For a simple environment that already meets most of them, targeted help with scope, gap validation, and the self-assessment may be enough.
Environments with real gaps can still need remediation, documentation, and identity work. What should raise an eyebrow is a provider selling a full managed program before establishing which situation you're in.
### **Level 2: What DoD Contractors Face**
[DoD contractors](https://www.motherbearsecurity.com/blog/dod-cmmc-requirements) handling CUI face 110 requirements, heavy documentation, and evidence expectations. Ask how many engagements at the same level they've completed and how those ended.
One current note: since July 13, 2026, [CMMC Phase 2 has been suspended](https://www.war.gov/News/Releases/Release/Article/4542329/forging-the-arsenal-of-freedom-department-of-war-suspends-cmmc-phase-ii-require/), and only Level 1 (Self) and Level 2 (Self) may currently be designated. A provider telling you the pause means waiting is giving bad advice.
## **From Full Compliance to Competitive Advantage**
The contractors who get most from these relationships treat them as capability building rather than outsourcing.
A provider who leaves your team able to run the program has given you something durable. That matters most in an industry where prime contractors screen on compliance posture, and where contract eligibility for DoD contracts depends on holding a current status when required.
For suppliers touching critical infrastructure or sensitive programs, that capability is worth more than any single engagement.
Reaching full compliance is the requirement. Being able to prove it quickly, without a three-week scramble, is the competitive advantage that wins defense contracts.
## **How MotherBear Keeps Your CMMC Compliance Program Yours**
Whichever provider you choose, the compliance record should live somewhere that doesn't change hands when the contract does.
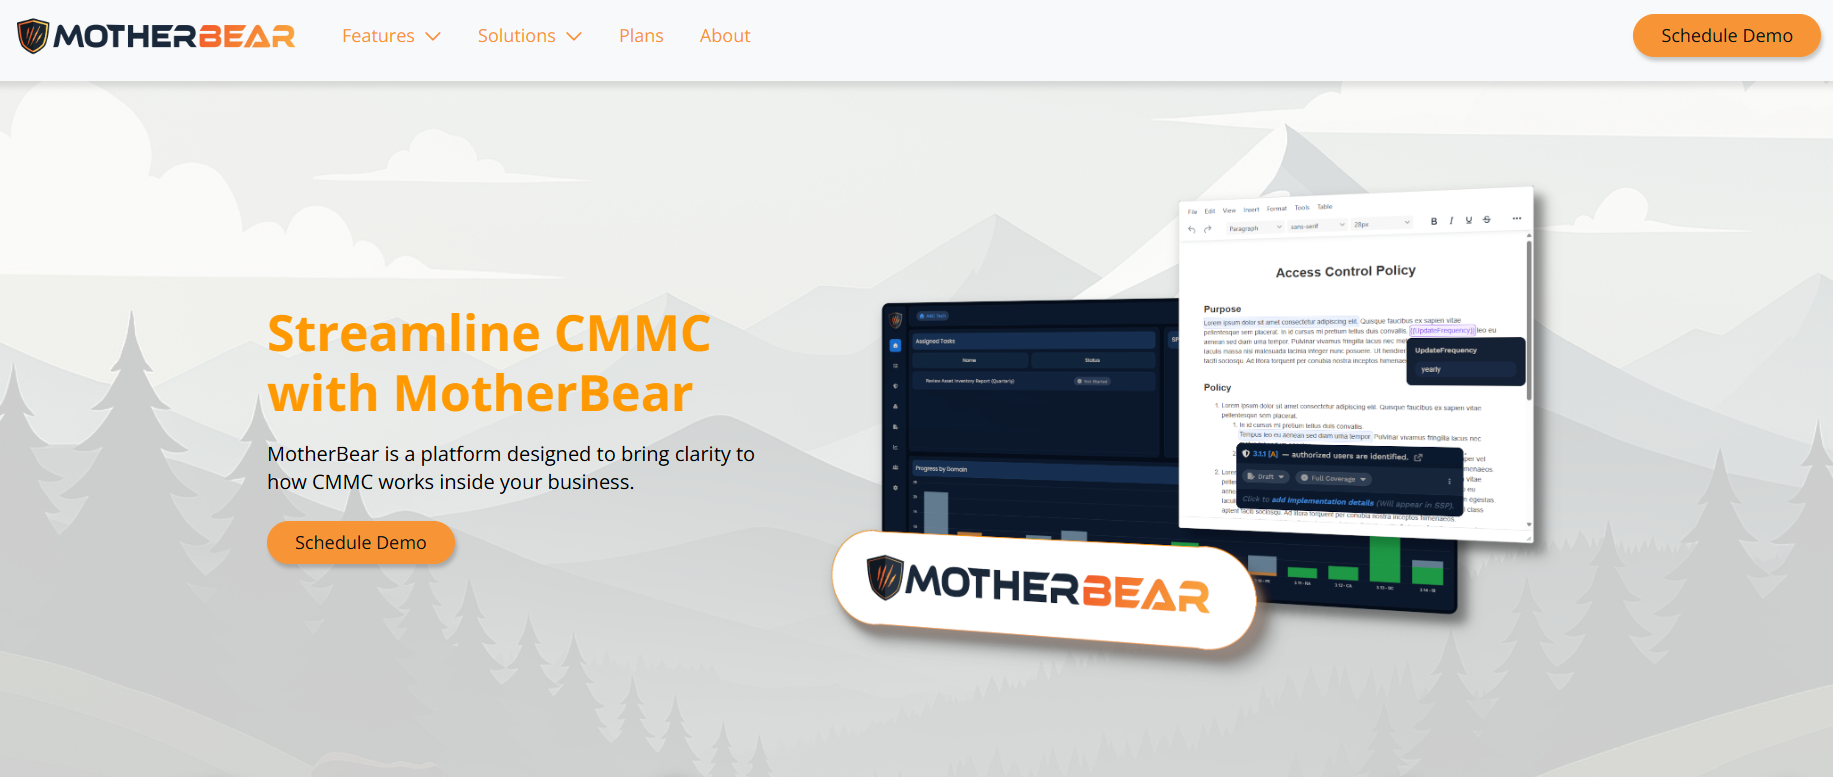
[MotherBear](https://www.motherbearsecurity.com/schedule-demo) gives defense contractors that workspace: requirement status against NIST 800-171, an evidence repository tied to what each artifact proves, SSP and policy materials, and remediation tasks with owners.
It also works from the provider's side. Consultants and MSPs running multiple contractor programs get a consistent structure per client, which is what makes an engagement transferable rather than sticky.
[***Book a demo and see how MotherBear keeps your program independent of who helps you run it.***](https://www.motherbearsecurity.com/schedule-demo)
## **FAQs About How to Choose a CMMC Provider**
### **How much does it cost to get CMMC-compliant?**
Cost tracks your environment rather than your headcount. The drivers are how much CUI you handle, how your systems are architected, how much already meets the requirements, and how much remediation a gap assessment uncovers.
Level 1 is comparatively inexpensive. Level 2 involves technical remediation, documentation, tooling, and often outside support. Budget separately for remediation rather than treating the readiness engagement as the full cost.
### **How hard is it to get CMMC-certified?**
The difficulty is sustained effort rather than technical complexity. Most requirements are ordinary security practice, but implementing 110 of them, documenting each, evidencing them, and keeping that current is a long project.
A good provider compresses the timeline and prevents expensive scoping mistakes. They don't remove the internal work, and one claiming otherwise is overselling.
### **Who provides CMMC assessments?**
When the Level 2 certification path applies, those assessments are conducted by authorized or accredited C3PAOs, with Level 3 handled by the government's DIBCAC. Under the current Phase 1 pause, applicable Level 2 requirements use self-assessment instead, which the contractor conducts.
RPOs, MSPs, and managed security service providers can support readiness but cannot issue a CMMC certificate, and a firm that consulted for you within the previous three years cannot perform your Level 2 certification assessment.
### **What is the difference between CMMC 2.0 Level 2 and Level 3?**
Level 2 covers CUI and requires the 110 requirements from [NIST 800-171](https://www.motherbearsecurity.com/blog/what-is-nist-800-171). Level 3 applies to a narrow set of programs handling the most sensitive information, adds selected requirements aimed at advanced persistent threats, and is assessed by the government.
Most contractors never encounter Level 3. If a provider suggests you need it without pointing to a specific contract requirement, ask which one.
## Need a CMMC Provider?
Book a demo of MotherBear to see how you can simplify CMMC
[Schedule Demo](https://www.motherbearsecurity.com/schedule-demo)
## Read On
[](https://www.motherbearsecurity.com/blog/cmmc-for-dod-suppliers)
### [CMMC for DoD Suppliers: What It Means and What to Do Now](https://www.motherbearsecurity.com/blog/cmmc-for-dod-suppliers)
For most suppliers, Cybersecurity Maturity Model Certification (CMMC) doesn't arrive as a policy...
[](https://www.motherbearsecurity.com/blog/cmmc-assessment-guide)
### [CMMC Assessment Guide: What to Expect and How to Prepare](https://www.motherbearsecurity.com/blog/cmmc-assessment-guide)
Not every Cybersecurity Maturity Model Certification (CMMC) assessment follows the same process....
[](https://www.motherbearsecurity.com/blog/cmmc-readiness)
### [CMMC Readiness: How to Prepare Before Assessment](https://www.motherbearsecurity.com/blog/cmmc-readiness)
Here's the thing about Cybersecurity Maturity Model Certification (CMMC): the work doesn't start...

#### Pages
[Home](https://www.motherbearsecurity.com)
[Plans](https://www.motherbearsecurity.com/plans)
[About](https://www.motherbearsecurity.com/about)
[Blog](https://www.motherbearsecurity.com/blog)
#### Features
[Requirements Tracking](https://www.motherbearsecurity.com/features/requirements-tracking)
[Documentation Builder](https://www.motherbearsecurity.com/features/documentation-builder)
[Evidence Repository](https://www.motherbearsecurity.com/features/evidence-repository)
[Task Management](https://www.motherbearsecurity.com/features/task-management)
#### Solutions
[For Defense Contractors](https://www.motherbearsecurity.com/solutions/defense-contractors)
[For Managed Service Providers](https://www.motherbearsecurity.com/solutions/managed-service-providers)
[For CMMC Professionals](https://www.motherbearsecurity.com/solutions/cmmc-professionals)
---
© 2026 Mother Bear Security, Inc. All rights reserved.
Privacy Policy
```json
{
"@context" : "https://schema.org",
"@type" : "BlogPosting",
"author" : {
"@type" : "Person",
"name" : "Nick Marteney",
"url" : "https://www.motherbearsecurity.com/blog/author/nick-marteney"
},
"dateModified" : "2026-10-30T11:57:16.151Z",
"datePublished" : "2026-10-30T11:57:16.000Z",
"headline" : "How to Choose a CMMC Provider: A Buyer's Checklist",
"image" : [ "https://www.motherbearsecurity.com/hubfs/How%20to%20choose%20a%20CMMC%20provider.png" ],
"mainEntityOfPage" : {
"@id" : "https://www.motherbearsecurity.com/blog/how-to-choose-a-cmmc-provider",
"@type" : "WebPage"
},
"publisher" : {
"@type" : "Organization",
"logo" : {
"@type" : "ImageObject",
"url" : "https://www.motherbearsecurity.com/hubfs/mbs-logo-transparent-h128.png"
},
"name" : "Mother Bear Security"
}
}
```