---
title: "CMMC Challenges: What Goes Wrong and How to Fix It"
description: Explore the most common CMMC challenges and learn how to overcome them. Discover how MotherBear can help obtain and maintain compliance.
image: https://www.motherbearsecurity.com/hubfs/CMMC%20Challenges.png
---
[](https://www.motherbearsecurity.com/)
- Features
- [Requirements Tracking Understand how and why you meet requirements](https://www.motherbearsecurity.com/features/requirements-tracking)
- [Documentation Builder Tools to streamline creating Policies, Procedures and your SSP](https://www.motherbearsecurity.com/features/documentation-builder)
- [Evidence Repository Store evidence with ease and ensure you are audit ready](https://www.motherbearsecurity.com/features/evidence-repository)
- [Task Management Assign, track, and manage tasks across your team](https://www.motherbearsecurity.com/features/task-management)
- Solutions
- [For Defense Contractors Purpose built for the Defense Industrial Base](https://www.motherbearsecurity.com/solutions/defense-contractors)
- [For Managed Service Providers Simplify program management for you and your clients](https://www.motherbearsecurity.com/solutions/managed-service-providers)
- [For CMMC Professionals Use tools that help you provide the best value to your clients](https://www.motherbearsecurity.com/solutions/cmmc-professionals)
- [Plans](https://www.motherbearsecurity.com/plans)
- [About](https://www.motherbearsecurity.com/about)
[Schedule Demo](https://www.motherbearsecurity.com/schedule-demo)
# CMMC Challenges: What Goes Wrong and How to Fix It
November 02, 2026

## Table of Contents
1. [TL;DR](https://www.motherbearsecurity.com/blog/cmmc-challenges#tldr)
2. [Why CMMC Compliance Challenges Aren't Only Technical](https://www.motherbearsecurity.com/blog/cmmc-challenges#Why-CMMC-Challenges)
3. [Common CMMC Compliance Challenges and the CMMC Requirements Behind Them](https://www.motherbearsecurity.com/blog/cmmc-challenges#Common-Challenges)
4. [Compliance Reporting: What Happens When the CMMC Assessment Process Goes Wrong](https://www.motherbearsecurity.com/blog/cmmc-challenges#Compliance-Reporting)
5. [How to Achieve CMMC Compliance With a Roadmap That Survives](https://www.motherbearsecurity.com/blog/cmmc-challenges#How-to-Achieve)
6. [How MotherBear Closes the Gap Between Claimed and Provable](https://www.motherbearsecurity.com/blog/cmmc-challenges#Motherbear)
7. [FAQs About CMMC Challenges](https://www.motherbearsecurity.com/blog/cmmc-challenges#FAQs)
DoD contractors spending real money to protect [Controlled Unclassified Information](https://www.motherbearsecurity.com/blog/what-is-cui) (CUI) are investing more in Cybersecurity Maturity Model Certification (CMMC) compliance than ever, reporting stronger programs and higher scores, and trusting those numbers far less than they did a year ago.
[CyberSheath's 2026 State of the Defense Industrial Base Report](https://cybersheath.com/resources/downloads/2026-state-of-the-defense-industrial-base-protecting-the-mission/) put figures on it. Only around two-thirds of contractors who submitted self-assessment scores this year said they were confident those scores reflect their actual cybersecurity posture, down sharply from the year before.
The median respondent rated their [CMMC readiness](https://www.motherbearsecurity.com/blog/cmmc-readiness) roughly at 70%.
That gap between what gets submitted and what teams believe is the real story of CMMC challenges. It isn't that contractors can't configure multi-factor authentication. It's that they can't always prove what they've claimed.
This guide walks through the problems that actually stall programs and cause assessments to fail, why each one happens, and how to fix it.
Many of them have less to do with sophisticated security engineering, or with cyber threats themselves, than with how the work gets scoped, documented, evidenced, and owned.
## **TL;DR**
- Many of the hardest CMMC challenges are organizational as much as technical: scoping, ownership, documentation, and evidence matter alongside the security controls themselves.
- Scoping errors can be among the most expensive mistakes, because every downstream decision inherits them.
- Outdated documentation is a common source of assessment problems, and it happens quietly.
- Sustaining compliance between assessments is where programs begin to drift, because systems, configurations, responsibilities, and evidence change faster than the documentation covering the required security controls gets updated.
- [MotherBear](https://www.motherbearsecurity.com/schedule-demo) closes the gap between claimed and provable by keeping requirement status, evidence, and documentation connected in one workspace.
## **Why CMMC Compliance Challenges Aren't Only Technical**
Many of the hardest CMMC failures aren't purely technical. Organizations can have capable security teams and still struggle, because scope, ownership, documentation, and evidence don't line up with the controls they've implemented.
What breaks is everything around the technical controls. Who owns them, whether anyone wrote down how they work, whether the evidence exists, and whether the description still matches the environment six months later.
Control implementation is the visible half of the job. Security measures can be technically implemented and still assessed NOT MET if you can't provide sufficient evidence that the applicable assessment objectives are satisfied.
That's why a company with strong security can fail an assessment while a less sophisticated one passes. CMMC measures demonstrated implementation rather than capability, and each requirement contains multiple assessment objectives that all have to be satisfied for the requirement to be MET.
Compliance failure usually lives in that distance between what's true and what's provable.
It also explains the confidence gap. Teams know their security is decent. They're much less sure they could prove it line by line if someone asked tomorrow.
## **Common CMMC Compliance Challenges and the CMMC Requirements Behind Them**
Under CMMC 2.0, the security requirements themselves are well documented. These are the problems that show up around them, roughly in the order they tend to bite.
### **Scoping the CUI Environment**
Scoping errors are expensive because everything downstream inherits them.
Over-scoping applies CUI controls to the entire network, multiplying cost and assessment surface beyond what [CMMC requires](https://www.motherbearsecurity.com/blog/dod-cmmc-requirements). Under-scoping misses systems that hold CUI, leaving security gaps that surface as critical deficiencies at exactly the wrong moment.
The fix is to map data flows before touching a single control. Identify every place CUI is created, stored, processed, and transmitted, including cloud services and external service providers.
Only then run a gap analysis to identify gaps against the requirements that actually apply. Segmentation can shrink what's in scope legitimately, but declaring assets out of scope because it's convenient just relocates the compliance gaps.
### **A CMMC Compliance Roadmap Nobody Updated**
A System Security Plan (SSP) written 18 months ago and never revised describes a company that no longer exists, and the same goes for the roadmap built alongside it.
This is a quiet failure. Without a change-management process tied to compliance documentation, a firewall rule changes, a new SaaS tool arrives, or an engineer adjusts system configurations, and the SSP silently stops being accurate.
Assessors find the discrepancy by comparing your description against your actual system configurations, security settings, and system settings.
The fix is to treat the SSP as a living document with a named owner and a review trigger tied to change management. When system settings change, maintain documentation in the same week rather than the same year.
A document management system helps here, though the discipline matters more than the tooling.
### **Evidence Nobody Collected**
Contractors routinely implement a control properly and then can't demonstrate compliance, because the proof was never captured.
The controls run fine. The screenshots, logs, reports, and records that would show an assessor they run are scattered among inboxes and personal drives, or were never generated at all.
The fix is to collect [objective evidence](https://www.motherbearsecurity.com/blog/cmmc-objective-evidence) as work happens rather than once an assessment begins. Maintain detailed logs, file artifacts against the requirement each one proves, and date everything.
Automated tools can capture some of this continuously, which beats a scramble to reconstruct the last twelve months.
### **Nobody Can Assign Responsibility**
Requirements assigned to "IT" collectively belong to nobody specifically, and this is a common cause of stalled programs.
The pattern is recognizable: an initial assessment identifies gaps, a plan gets built, and then it slows because the person nominally responsible has a full-time job doing something else.
Resource constraints make it worse in smaller organizations, where security responsibilities get spread thin among people who were hired to do something different.
The fix is to assign responsibility per requirement, with named owners and dates. Give one person accountability for the compliance program overall.
Leadership also has to accept that compliance efforts displace other work rather than stacking on top of it.
### **Overly Permissive Access Rights**
Access control is a demanding assessment area because permissions tend to accumulate over time, and the cause is usually drift rather than negligence.
Privileged accounts multiply, contractors keep system access after projects end, and shared credentials survive because changing them would break something. Nobody decided any of this; it accrued.
The fix is to treat access management as a recurring process rather than a setup task. Run access reviews on a schedule, document an access control policy that reflects what you actually do, and use automated asset discovery to find the accounts and devices your inventory missed.
Automated management tools make this sustainable at scale, since manual reviews are what get skipped when the security risks feel abstract.
### **Audit Logs and Continuous Monitoring**
Level 2 expects logging that supports detecting and investigating security incidents, and many organizations discover their coverage is thinner than assumed.
Logs get generated but never reviewed, retention isn't sufficient to support monitoring and investigations, or critical systems aren't logging at all. Continuous monitoring becomes an aspiration rather than a practice, and the incident response plan sits untested in a folder.
Ongoing monitoring is what turns both from documents into evidence an assessor can examine.
The fix is to centralize logging so review is possible, set retention deliberately rather than by default, and document who reviews what and how often.
A security operations center or managed provider can carry the security monitoring load where internal capacity doesn't exist.
### **External Service Providers**
[Managed service providers](https://www.motherbearsecurity.com/blog/cmmc-for-msps) (MSPs) and cloud services become part of your [CMMC assessment](https://www.motherbearsecurity.com/blog/cmmc-assessment-guide) picture when they process, store, or transmit CUI or Security Protection Data.
Their services and assigned security responsibilities can then fall inside your assessment scope, which makes their third-party security practices your concern too.
The treatment depends on the provider. Cloud services handling CUI must meet security requirements equivalent to the Federal Risk and Authorization Management Program (FedRAMP) Moderate baseline under Defense Federal Acquisition Regulation Supplement (DFARS) clause 252.204-7012.
Services from a non-cloud external service provider handling CUI are assessed within your own scope instead. A provider touching neither CUI nor Security Protection Data isn't an external service provider for assessment purposes.
The trouble starts when responsibility is assumed rather than documented. Both sides think the other handles patching, or logging, or access reviews.
The fix is to document the relationship in your SSP and capture the split in a Customer Responsibility Matrix, so every requirement has a named owner on one side of the relationship or the other.
Confirm that cloud services handling CUI meet the requirements that apply to them, and include providers in your risk assessments rather than treating them as someone else's problem.
### **Sustaining Compliance After the Assessment**
The last challenge is the one nobody budgets for. Programs decay after the assessment because the pressure that built them disappears.
Systems change, staff turn over, and the compliance status that was accurate on submission day slowly stops being true. The next cycle can then become far more expensive than it needs to be.
The fix is to schedule regular internal audits, keep evidence collection continuous, and treat ongoing compliance as an operating function rather than a project with an end date. That cadence is what will ensure ongoing adherence once the deadline pressure lifts.
Organizations that maintain security and paperwork together carry far lower compliance risks into the next cycle.
## **Compliance Reporting: What Happens When the CMMC Assessment Process Goes Wrong**
Assessment failure isn't a single event with a single consequence, and the shape of it depends on your level. What gets reported is your compliance status, which is what contracting officers see.
At Level 1, covering [Federal Contract Information](https://www.motherbearsecurity.com/blog/what-is-fci) (FCI), there's no partial credit. All 15 requirements must be met, no remediation plans are permitted, and a single unmet item means no status.
At Level 2, you may use a formal Plan of Action and Milestones (POA&M) for eligible requirements, with conditional status requiring a score of at least 88 out of 110 and closeout within 180 days. Requirements that aren't eligible for deferral have to be met outright.
The commercial consequences run further than the assessment itself. Without the required status, you're not eligible for award on solicitations that require it, and primes increasingly screen subcontractors on their overall security posture before they'll consider a bid.
Assessment findings also have a habit of repeating. Failed audits usually trace back to the same root causes rather than new ones, which is why fixing the structure beats fixing individual controls.
There's a legal dimension too. Knowingly false compliance representations can create False Claims Act exposure, which is why the confidence gap matters beyond assessment readiness.
## **How to Achieve CMMC Compliance With a Roadmap That Survives**
Most of the challenges above share a root cause: a plan that existed on paper and then lost contact with the environment it described.
A roadmap that survives has four properties. It:
1. Starts from a real gap assessment of your current security posture rather than an assumption
2. Assigns every requirement an owner and a date
3. Produces evidence continuously rather than at the end
4. Has a maintenance cadence built in from the start
That structure matters more for organizations pursuing [CMMC compliance](https://www.motherbearsecurity.com/blog/what-is-cmmc-compliance) for the first time, since they have no prior cycle to learn from.
Budget alone doesn't solve the organizational problem. What separates the programs that run smoothly is being able to answer which requirements are met, who owns the open ones, and where the evidence lives.
## **How MotherBear Closes the Gap Between Claimed and Provable**
Nearly every challenge here comes back to the same structural problem: requirement status, evidence, and documentation live in different places, and nothing keeps them in sync.
That's what produces the confidence disconnect. A contractor can be genuinely secure and still be unsure what they'd hand an assessor, because assembling that answer means a week of archaeology.
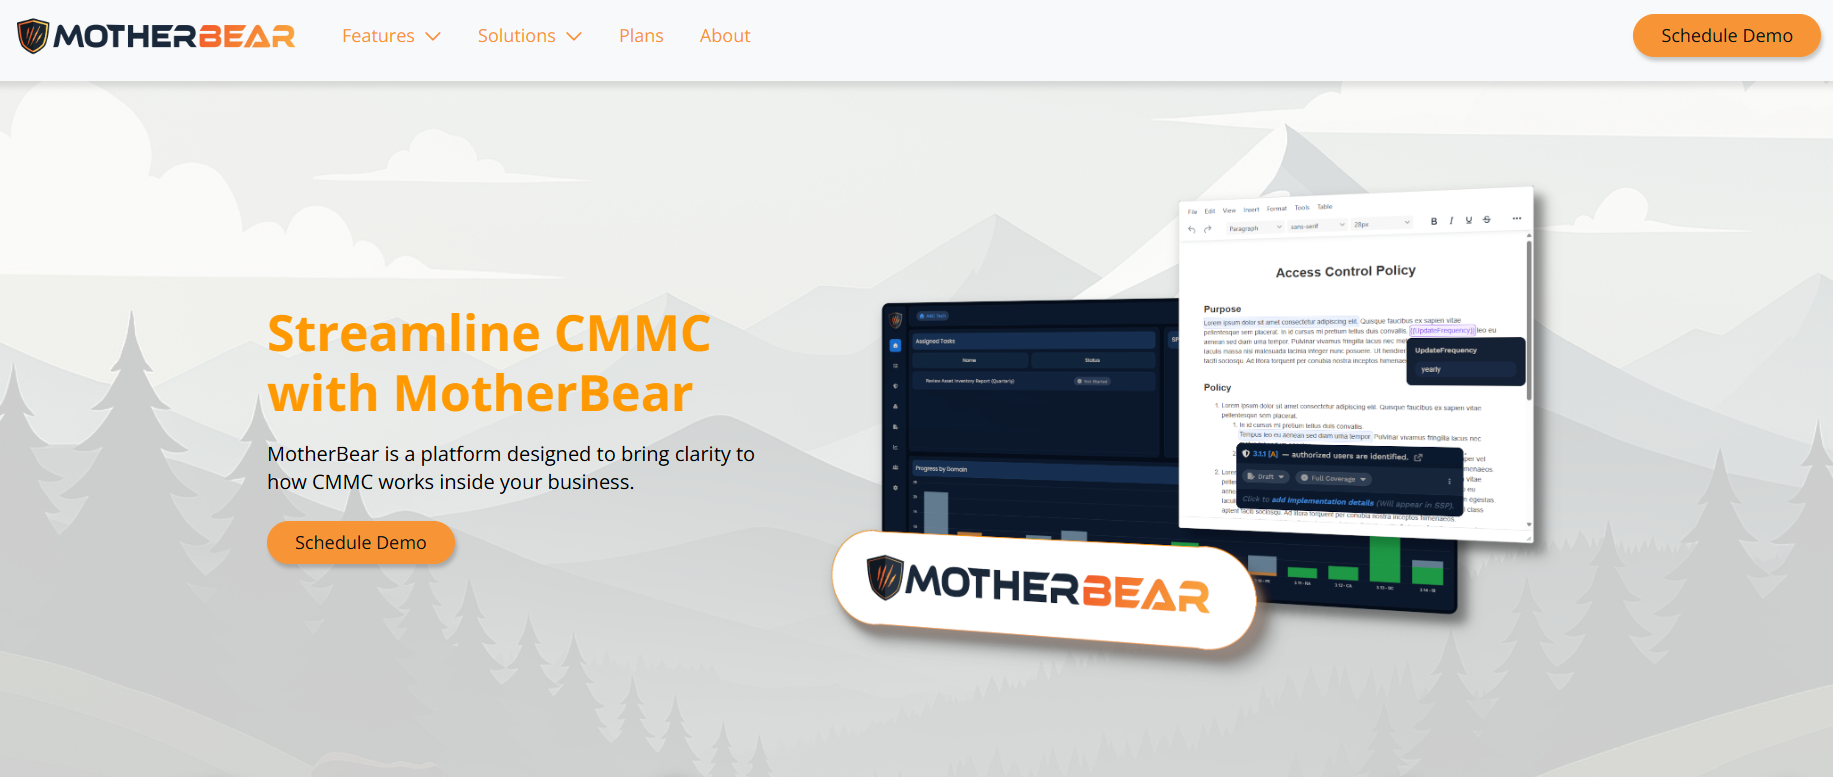
[MotherBear](https://www.motherbearsecurity.com/schedule-demo) gives defense contractors and their consultants one workspace for the whole picture.
Requirement status against the National Institute of Standards and Technology (NIST) standard 800-171, an evidence repository tied to what each artifact proves, SSP and policy materials, and remediation tasks with owners all sit together.
For a consultant carrying several client programs, that shared structure is also what makes recurring problems visible early, while there's still time to fix them cheaply.
[***Book a demo and see how MotherBear turns a compliance claim into something you can show.***](https://www.motherbearsecurity.com/schedule-demo)
## **FAQs About CMMC Challenges**
### **What happens if you fail CMMC?**
The result depends on the level and the findings. At Level 1, any unmet requirement prevents you from achieving the status, because no remediation plan is allowed.
At Level 2, you may receive Conditional Level 2 if you score at least 88 out of 110 and only eligible requirements remain on a formal Plan of Action and Milestones. Those items have to be closed through the appropriate closeout assessment within 180 days.
If you don't meet the conditions for Final or Conditional status, you won't hold the status that awards requiring it depend on. Remediating and reassessing costs time you usually don't have.
### **What are some common compliance challenges?**
Scoping errors, documentation that no longer matches the environment, missing evidence for controls that are genuinely implemented, unclear ownership, accumulated access rights, and thin audit logging.
The common pattern is that they're organizational rather than technical. The controls tend to work; what fails is the structure around proving they work and keeping them working.
### **How hard is CMMC compliance?**
The difficulty is sustained effort rather than technical complexity. Most individual requirements are ordinary security practice, but implementing 110 of them, documenting each one, evidencing them, and keeping all of that current is a long project.
Contractors with existing security frameworks find it manageable. Those starting from informal practices usually find the documentation harder than the technology.
### **What is the current status of CMMC?**
Phase 1 has been active since November 2025, with self-assessment requirements appearing in applicable contracts. On July 13, 2026, the [Department suspended Phase 2](https://dodcio.defense.gov/CMMC/) along with pending implementation milestones, and during the suspension only Level 1 (Self) and Level 2 (Self) may be designated.
Phase 1 obligations continue throughout the review, so self-assessments, results in the Supplier Performance Risk System (SPRS), and annual affirmations all remain in force.
## Facing CMMC challenges?
Book a demo of MotherBear to see how we can help you out
[Schedule Demo](https://www.motherbearsecurity.com/schedule-demo)

#### Pages
[Home](https://www.motherbearsecurity.com)
[Plans](https://www.motherbearsecurity.com/plans)
[About](https://www.motherbearsecurity.com/about)
[Blog](https://www.motherbearsecurity.com/blog)
#### Features
[Requirements Tracking](https://www.motherbearsecurity.com/features/requirements-tracking)
[Documentation Builder](https://www.motherbearsecurity.com/features/documentation-builder)
[Evidence Repository](https://www.motherbearsecurity.com/features/evidence-repository)
[Task Management](https://www.motherbearsecurity.com/features/task-management)
#### Solutions
[For Defense Contractors](https://www.motherbearsecurity.com/solutions/defense-contractors)
[For Managed Service Providers](https://www.motherbearsecurity.com/solutions/managed-service-providers)
[For CMMC Professionals](https://www.motherbearsecurity.com/solutions/cmmc-professionals)
---
© 2026 Mother Bear Security, Inc. All rights reserved.
Privacy Policy
```json
{
"@context" : "https://schema.org",
"@type" : "BlogPosting",
"author" : {
"@type" : "Person",
"name" : "Nick Marteney",
"url" : "https://www.motherbearsecurity.com/blog/author/nick-marteney"
},
"dateModified" : "2026-11-02T11:47:15.242Z",
"datePublished" : "2026-11-02T11:47:15.000Z",
"headline" : "CMMC Challenges: What Goes Wrong and How to Fix It",
"image" : [ "https://www.motherbearsecurity.com/hubfs/CMMC%20Challenges.png" ],
"mainEntityOfPage" : {
"@id" : "https://www.motherbearsecurity.com/blog/cmmc-challenges",
"@type" : "WebPage"
},
"publisher" : {
"@type" : "Organization",
"logo" : {
"@type" : "ImageObject",
"url" : "https://www.motherbearsecurity.com/hubfs/mbs-logo-transparent-h128.png"
},
"name" : "Mother Bear Security"
}
}
```